Cyber Security Strategy Framework: Step-By-Step Guide
Most organisations know they need better cyber security. Fewer know where to start. A cyber security strategy framework gives you that starting point, a structured, repeatable approach to identifying risks, setting priorities, and building defences that actually hold up when tested. Without one, security efforts tend to be reactive, patchy, and expensive. With one, every […]
10 Network Penetration Testing Services In The UK (2026)
Hiring the wrong pen testing provider can give you a false sense of security, or worse, leave critical vulnerabilities undiscovered. With network penetration testing services growing in demand across the UK, choosing a provider that actually understands your infrastructure and compliance requirements matters more than picking the cheapest quote. A thorough test should expose real […]
AWS Penetration Testing Policy: Permitted And Prohibited
Running penetration tests against your AWS-hosted infrastructure without understanding the AWS penetration testing policy can put your organisation at risk, not from attackers, but from AWS itself. Violating their Acceptable Use Policy could lead to service suspension or account termination, which is the opposite of what a security assessment is supposed to achieve. AWS has […]
How To Protect Business Data: 15 Fast Ways To Reduce Risk
Every business holds data that someone else wants. Customer records, financial information, intellectual property, employee details, it all has value, and criminals know it. Knowing how to protect business data isn’t optional anymore; it’s a core responsibility. Yet many organisations still rely on outdated practices or assume a basic antivirus solution is enough to keep […]
Types Of Data Security Threats: Examples And Prevention Tips
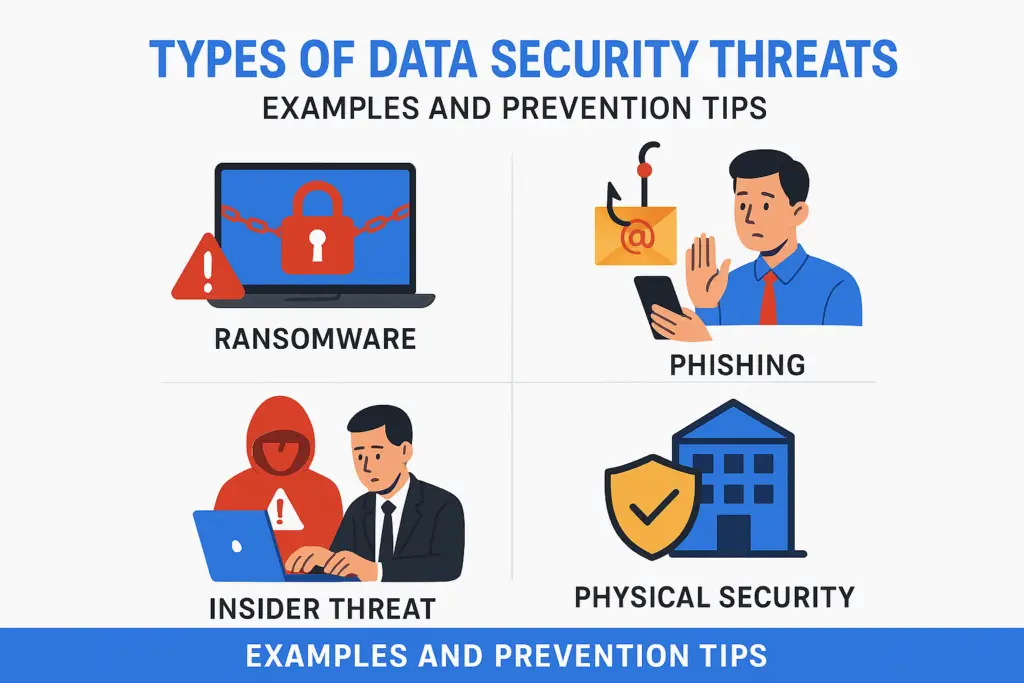
Every organisation holds data that someone else wants, customer records, financial information, intellectual property, credentials. The types of data security threats targeting that information have grown more varied and more damaging over the past decade. From ransomware that locks entire networks to phishing emails that trick a single employee into handing over login details, each […]
ServiceNow Business Continuity Management: Features & Setup
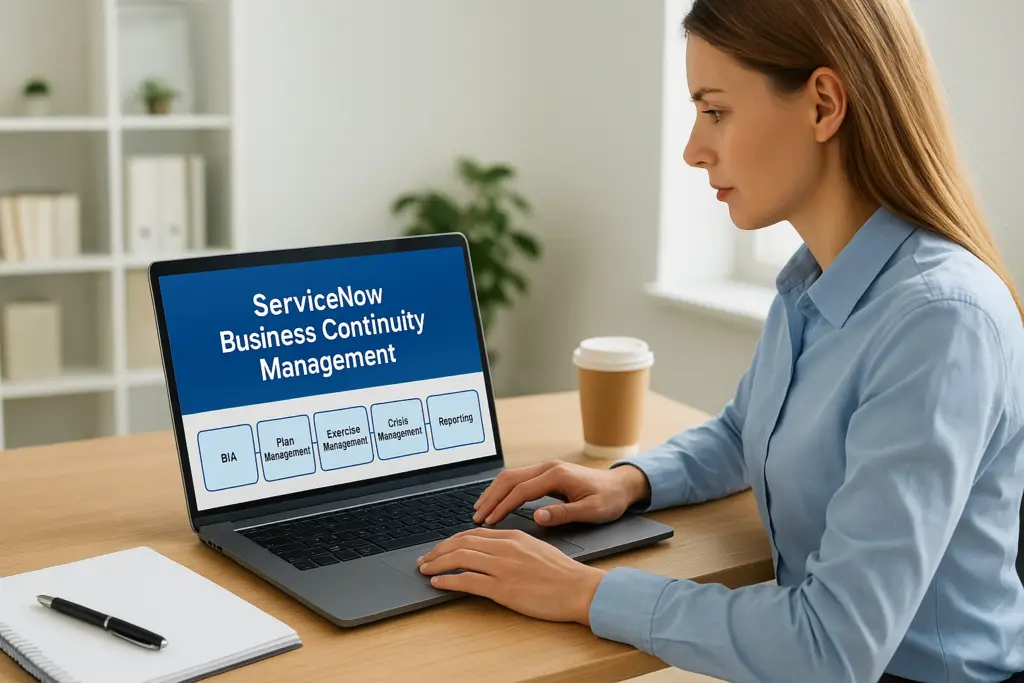
When a critical system goes down or a cyber incident strikes, the difference between a minor disruption and a full-blown crisis often comes down to planning. ServiceNow Business Continuity Management (BCM) is a module built to help organisations structure that planning, from business impact analysis through to recovery workflows, all within the ServiceNow platform. But […]
How To Create A Disaster Recovery Plan: Step-By-Step
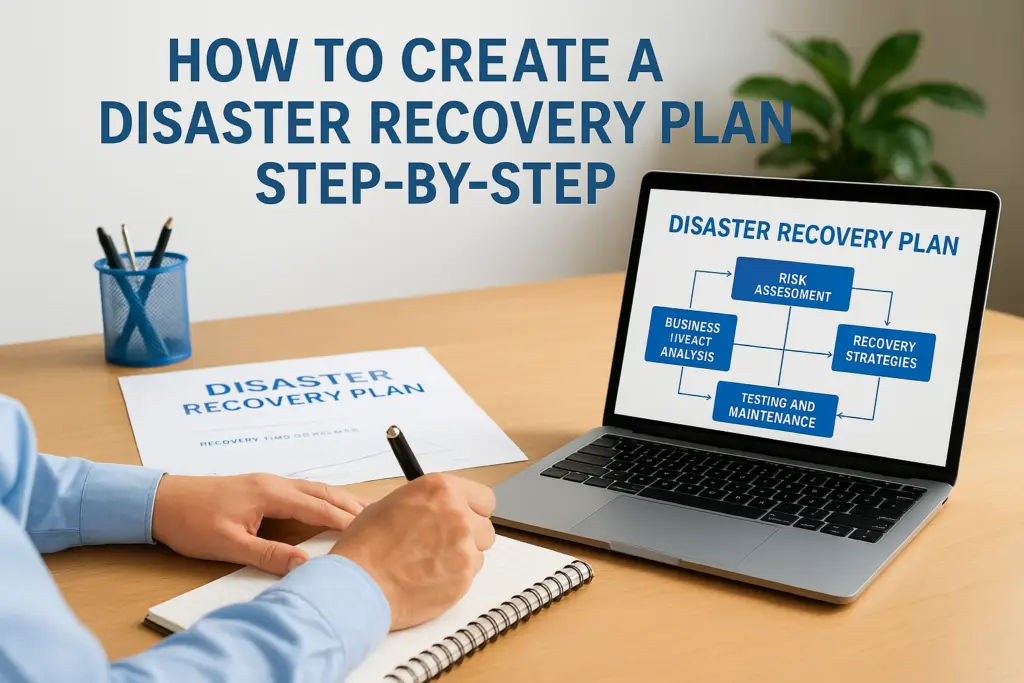
A single ransomware attack, server failure, or data breach can bring operations to a grinding halt, sometimes for days. The difference between a business that recovers quickly and one that struggles to survive often comes down to one thing: whether someone took the time to figure out how to create a disaster recovery plan before […]
Disaster Recovery Definition: DR Meaning, RTO & RPO Explained
A clear disaster recovery definition starts with a simple truth: every business depends on its IT systems, and those systems can fail. Hardware breaks, ransomware encrypts files, data centres flood. What matters is whether your organisation can get back on its feet, and how quickly. That’s exactly what disaster recovery (DR) addresses. DR isn’t just […]
6 Risk Assessment Framework Examples for UK Businesses
Choosing the right risk assessment framework can feel overwhelming when there are dozens of standards, models, and templates competing for your attention. Most UK businesses know they need a structured approach to identifying and managing risk, especially cyber risk, but figuring out where to start is the hard part. That’s exactly why we’ve put together […]
What Is GDPR Compliance? Principles, Requirements & Steps
Every organisation that handles personal data belonging to individuals in the UK or EU needs to understand what is GDPR compliance, and more importantly, what it actually takes to achieve it. The General Data Protection Regulation sets out strict rules for how businesses collect, store, process, and share personal data. Getting it wrong carries real […]