
Hiring the wrong pen testing provider can give you a false sense of security, or worse, leave critical vulnerabilities undiscovered. With network penetration testing services growing in demand across the UK, choosing a provider that actually understands your infrastructure and compliance requirements matters more than picking the cheapest quote. A thorough test should expose real weaknesses before attackers do, not just tick a box for your next audit.
At TrustedIA, we deliver penetration testing as part of our managed cybersecurity services, backed by over 30 years of hands-on experience in IT security and ISO 27001 implementation. We’ve seen firsthand what separates a useful pen test from a superficial one. That perspective shaped this list.
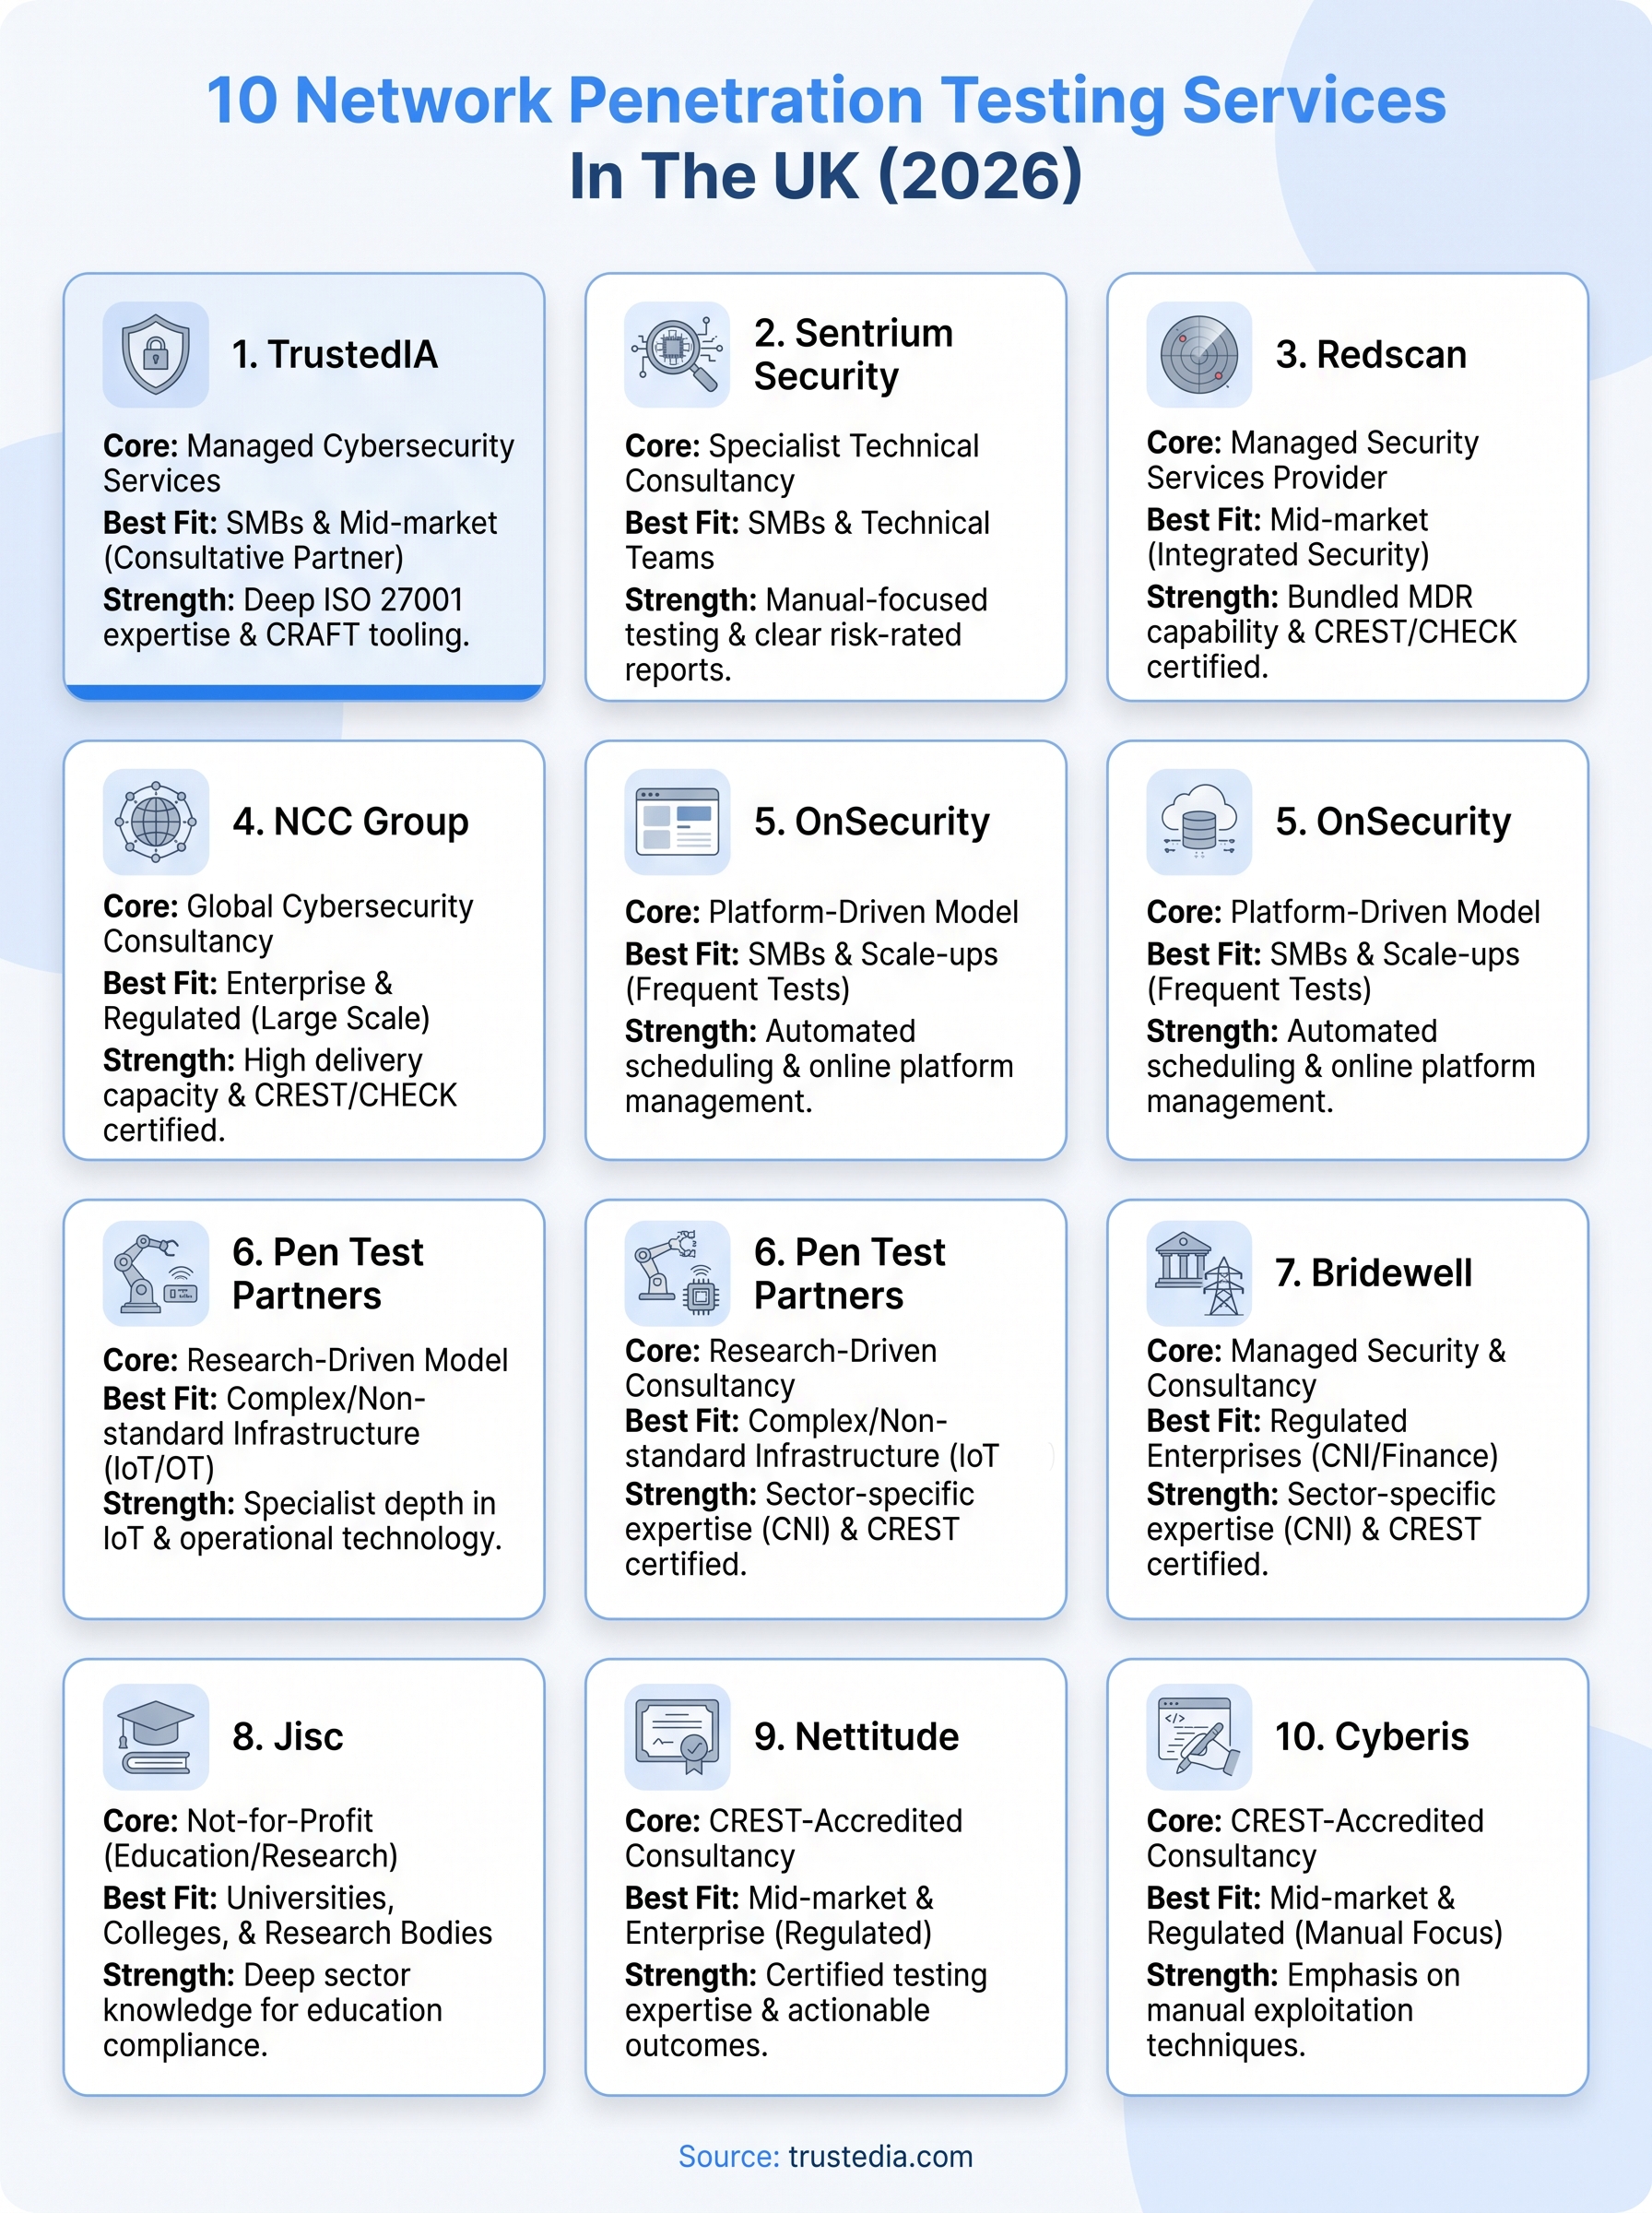
Below, we’ve compiled 10 network penetration testing providers operating in the UK right now, including what each one does well and who they’re best suited for. Whether you’re an SMB without an in-house security team or an enterprise preparing for certification, this guide will help you shortlist providers worth speaking to.
1. TrustedIA
TrustedIA provides managed cybersecurity services from a team with over 30 years of experience, and network penetration testing sits at the core of their vulnerability management offering. Their solution-agnostic approach means they recommend what actually works for your environment, not what suits a vendor relationship.
What they offer for network penetration testing
TrustedIA delivers both internal and external network penetration testing, covering wired and wireless infrastructure, cloud environments, and hybrid setups. Their proprietary CRAFT tooling supports posture assessment alongside manual testing techniques for a thorough picture of your exposure.
How they run a typical engagement
The process starts with scoping your environment and defining clear objectives before any testing begins. TrustedIA’s consultants use a structured methodology that combines automated scanning with manual exploitation attempts, then deliver a clear report with prioritised remediation steps.
TrustedIA provides a debrief session after every engagement so your team understands exactly what was found and what to fix first.
Strengths and trade-offs
Deep ISO 27001 expertise means findings are framed in a compliance context, which is useful if certification is on your roadmap. The trade-off is that TrustedIA is a specialist managed services provider rather than a large-scale firm, so very high-volume concurrent engagements may need advance planning.
Best fit for
TrustedIA works well for SMBs and mid-market organisations that want a hands-on, consultative partner rather than a transactional vendor. Insurers and loss adjusters already using their CyberSOS incident response service also benefit from pairing that with proactive network penetration testing services.
Compliance and standards coverage
Testing aligns with ISO/IEC 27001 requirements and supports Cyber Essentials Plus readiness. Their auditors understand the control framework in detail, so gaps identified during testing map directly to the relevant ISO controls your organisation needs to address.
Typical pricing and lead time
Pricing is scoped per engagement based on the size and complexity of your network. Contact TrustedIA directly for a tailored quote. Lead times are typically short given their managed services model and dedicated consultant team.
What you need to prepare
Have a network diagram and an up-to-date asset inventory ready before the scoping call. You should also confirm whether you need internal testing, external testing, or both, and identify any systems that must remain out of scope during the engagement.
2. Sentrium Security
Sentrium Security is a UK-based penetration testing consultancy that focuses on technical security assessments. They operate as a specialist boutique firm, which means their consultants tend to carry deep hands-on experience rather than a generalist IT background.
What they offer for network penetration testing
Sentrium provides internal and external network penetration testing services, covering infrastructure, web applications, and cloud environments. Their team conducts manual testing alongside automated scanning to surface vulnerabilities that tools alone would miss.
How they run a typical engagement
Engagements follow a structured scoping process before any testing begins. Consultants then deliver findings in a clear report that includes a risk-rated vulnerability list and actionable remediation guidance.
Their reports are written for both technical teams and business stakeholders, so critical findings reach the right people without getting buried in technical detail.
Strengths and trade-offs
Specialist focus on penetration testing means you get dedicated testers rather than a generalist team. The trade-off is that broader managed security services such as ongoing SOC monitoring sit outside their core offering.
Best fit for
Sentrium suits SMBs and technical teams that want a focused, hands-on assessment without engaging a large enterprise consultancy.
Compliance and standards coverage
Testing supports Cyber Essentials Plus and ISO 27001 audit preparation, helping you close control gaps before a formal certification review.
Typical pricing and lead time
Pricing varies by scope and network size. Contact Sentrium directly for a tailored quote, as lead times depend on current capacity.
What you need to prepare
Prepare a current asset inventory and confirm your testing boundaries, including which systems are explicitly in or out of scope, before the engagement begins.
3. Redscan
Redscan is a UK-based managed security services provider that delivers network penetration testing services alongside a broader cybersecurity portfolio including threat intelligence and managed detection. They combine certified in-house testers with an integrated security operations function.
What they offer for network penetration testing
Redscan provides internal and external network penetration testing, covering infrastructure, wireless environments, and cloud-connected systems. Their testers hold CREST and CHECK certifications, which sets a recognised quality benchmark for the assessments they deliver.
How they run a typical engagement
Engagements open with a detailed scoping session to define targets, testing windows, and rules of engagement. Consultants then conduct the assessment and produce a risk-rated report that maps vulnerabilities to practical remediation steps your team can act on quickly.
Their post-assessment debrief helps your team understand which findings carry the most immediate risk, rather than leaving you to interpret a dense technical report alone.
Strengths and trade-offs
Integrated MDR capability means you can move from a point-in-time test into ongoing threat monitoring with the same provider. The trade-off is that their bundled service model may not suit organisations that need a standalone test without a longer-term managed services commitment.
Best fit for
Redscan fits mid-market businesses that want to combine penetration testing with continuous security monitoring under one provider relationship.
Compliance and standards coverage
Their testing supports Cyber Essentials Plus readiness and ISO 27001 control gap identification before a formal certification audit.
Typical pricing and lead time
Pricing is scoped per engagement. Contact Redscan directly for a tailored quote based on your network size and testing requirements.
What you need to prepare
Prepare a current network topology diagram and a confirmed asset list, and clarify whether you need wireless or cloud environments included in the scope before your first call.
4. NCC Group
NCC Group is a global cybersecurity consultancy headquartered in Manchester, making them one of the largest UK-originating security firms operating today. They carry substantial testing resource across multiple countries and sectors.
What they offer for network penetration testing
NCC Group delivers infrastructure and network penetration testing services covering internal networks, external perimeters, wireless systems, and cloud environments. Their testers hold CREST and CHECK certifications, ensuring assessments meet recognised UK government-backed quality standards.
How they run a typical engagement
Engagements begin with a formal scoping exercise that defines targets, testing windows, and rules of engagement. Once testing concludes, you receive a risk-rated findings report alongside mapped remediation recommendations and a structured technical debrief.
Their scale means they can resource large or time-sensitive engagements that smaller specialist firms would struggle to accommodate.
Strengths and trade-offs
Deep technical expertise and significant delivery capacity mean NCC Group handles complex, multi-site testing programmes with ease. The trade-off is that their large-firm structure can feel less consultative than a specialist boutique provider, particularly for smaller organisations wanting a closer working relationship.
Best fit for
NCC Group suits enterprise-level organisations and regulated businesses that need high-volume or multi-jurisdictional testing programmes run to a consistent standard.
Compliance and standards coverage
Their testing supports ISO 27001 and Cyber Essentials Plus, alongside various sector-specific regulatory frameworks including financial services requirements.
Typical pricing and lead time
Pricing is engagement-specific and typically reflects enterprise-scale scoping. Contact NCC Group directly for a tailored quote and confirmed lead time.
What you need to prepare
Prepare a detailed network inventory and topology map, and flag any regulatory constraints or system exclusions clearly before the scoping call begins.
5. OnSecurity
OnSecurity is a UK-based penetration testing firm that operates through a platform-driven model, combining automated scheduling with certified manual testing to make recurring assessments more accessible for growing businesses.
What they offer for network penetration testing
OnSecurity delivers internal and external network penetration testing services, covering on-premises infrastructure and cloud-connected environments. Their platform lets you schedule and manage engagements directly, which cuts the administrative friction out of booking tests.
How they run a typical engagement
You define your scope through their online platform, and their certified testers then conduct the assessment and upload findings to your dashboard. Reports include risk-rated vulnerabilities with clear remediation guidance attached to each finding.
Their platform makes it straightforward to track open findings and monitor remediation progress in one place, rather than chasing updates across email threads.
Strengths and trade-offs
Platform-led delivery speeds up scoping and reporting for teams that test frequently. The trade-off is that the self-service model can feel less consultative than a firm that leads scoping conversations in person.
Best fit for
OnSecurity suits SMBs and scale-ups that run frequent testing cycles and want a repeatable, low-friction process each time.
Compliance and standards coverage
Their testing supports Cyber Essentials Plus and ISO 27001 gap identification ahead of certification audits.
Typical pricing and lead time
Pricing is published on their platform, which is more transparent than most providers. Lead times are generally short due to the automated scheduling model.
What you need to prepare
Confirm your network scope and IP ranges before scheduling, and flag any systems that must stay out of scope to avoid testing windows touching restricted infrastructure.
6. Pen Test Partners
Pen Test Partners is a UK-based cybersecurity firm known for its research-driven approach to security testing. They publish a significant volume of original vulnerability research and bring that investigative mindset directly into client engagements.
What they offer for network penetration testing
Pen Test Partners delivers internal and external network penetration testing services across a range of environments, including on-premises infrastructure, industrial control systems, and connected devices. Their testers hold CREST certifications and cover specialist areas such as IoT and operational technology alongside standard network assessments.
How they run a typical engagement
Engagements follow a structured scoping and rules-of-engagement process before any testing begins. Findings land in a risk-rated written report with clear remediation guidance, supported by a debrief your technical team can use to prioritise fixes.
Their background in vulnerability research means testers often surface attack paths that standard scanning tools would not flag on their own.
Strengths and trade-offs
Specialist depth in IoT, maritime, and operational technology sets Pen Test Partners apart from most general-purpose firms. The trade-off is that their niche focus may be more than you need if your environment is a straightforward corporate network.
Best fit for
Pen Test Partners works well for organisations running complex or non-standard infrastructure, including those operating connected devices, industrial systems, or sector-specific technology.
Compliance and standards coverage
Their testing supports Cyber Essentials Plus and ISO 27001 control gap identification ahead of formal certification assessments.
Typical pricing and lead time
Pricing is scoped per engagement. Contact Pen Test Partners directly for a tailored quote based on your environment and testing requirements.
What you need to prepare
Prepare a full asset list that covers any connected or non-standard devices, and clarify which specialist environments need testing before your scoping call.
7. Bridewell
Bridewell is a UK-based managed security services and consultancy firm with a strong presence in regulated sectors including financial services, utilities, and central government. They combine penetration testing with broader security transformation programmes.
What they offer for network penetration testing
Bridewell delivers internal and external network penetration testing services across on-premises and cloud infrastructure. Their testers hold CREST certifications, and the firm brings sector-specific knowledge into each assessment rather than applying a generic testing template.
How they run a typical engagement
Engagements open with a structured scoping session that defines targets, testing windows, and rules of engagement. Consultants conduct the assessment and deliver a risk-rated report with mapped remediation guidance, followed by a debrief to walk your team through the findings.
Their background in regulated sectors means findings are framed with compliance and operational risk in mind, not just technical severity scores.
Strengths and trade-offs
Sector-specific expertise in critical national infrastructure and financial services gives Bridewell a clear edge in heavily regulated environments. The trade-off is that their enterprise focus may leave smaller organisations finding them over-specified for a straightforward network assessment.
Best fit for
Bridewell suits regulated enterprises and public sector organisations that need penetration testing delivered within a recognised compliance and governance framework.
Compliance and standards coverage
Their testing supports ISO 27001 and Cyber Essentials Plus, alongside sector-specific frameworks including NCSC guidance for critical infrastructure operators.
Typical pricing and lead time
Pricing is scoped per engagement. Contact Bridewell directly for a tailored quote and confirmed lead time based on your network size and environment.
What you need to prepare
Prepare a current network topology diagram and a confirmed asset inventory, and flag any regulatory constraints or sensitive systems before your scoping call begins.
8. Jisc
Jisc is a UK-based not-for-profit organisation that delivers digital technology and cybersecurity services to the higher education, further education, and research sectors. Their penetration testing offering is built specifically around the compliance and infrastructure demands of educational institutions.
What they offer for network penetration testing
Jisc provides network penetration testing services designed for universities, colleges, and research organisations. Their assessments cover on-premises infrastructure and internet-facing systems, with testing methodologies tailored to the specific risk profile of educational networks.
How they run a typical engagement
Engagements begin with a structured scoping process to establish targets and rules of engagement. Jisc’s team then conducts the assessment and delivers a written findings report with risk-rated vulnerabilities and clear remediation guidance your team can act on.
Their sector-specific context means findings are interpreted through the lens of education compliance requirements, not generic commercial frameworks.
Strengths and trade-offs
Deep familiarity with education sector infrastructure gives Jisc a clear advantage when testing institutions that run complex, open-access networks. The trade-off is that their sector focus makes them a poor fit for businesses outside education and research.
Best fit for
Jisc works best for universities, colleges, and research bodies that need penetration testing from a provider that understands their unique network architecture and compliance obligations.
Compliance and standards coverage
Their testing supports Cyber Essentials Plus and sector-relevant frameworks including NCSC guidance for educational institutions.
Typical pricing and lead time
Pricing is available on request directly through Jisc. Lead times vary based on current demand across their member organisations.
What you need to prepare
Prepare a current asset inventory and network diagram, and confirm which internet-facing systems and internal segments fall within your testing scope before your initial call.
9. Nettitude
Nettitude is a CREST-accredited cybersecurity consultancy operating across the UK and internationally, with a strong track record in delivering technical security assessments for businesses in regulated industries. They combine certified testing expertise with a clear focus on actionable outcomes.
What they offer for network penetration testing
Nettitude delivers internal and external network penetration testing services covering on-premises infrastructure, cloud environments, and hybrid setups. Their certified testers conduct manual assessments alongside automated techniques to surface vulnerabilities that affect your real attack surface.
How they run a typical engagement
Engagements start with a structured scoping call to define your targets, testing windows, and rules of engagement. Once testing completes, Nettitude delivers a risk-rated report with prioritised remediation guidance and a debrief session to walk your team through the findings.
Their CREST accreditation means testing methodology meets a recognised quality benchmark, which carries weight when presenting results to auditors or insurers.
Strengths and trade-offs
CREST-accredited delivery and strong sector experience make Nettitude a dependable choice for regulated businesses. The trade-off is that their enterprise-oriented model may feel over-specified for very small organisations seeking a quick, narrowly scoped assessment.
Best fit for
Nettitude suits mid-market and enterprise organisations in regulated sectors that need certified, thorough testing delivered to a consistent standard.
Compliance and standards coverage
Their testing supports ISO 27001 and Cyber Essentials Plus preparation, alongside sector-specific compliance requirements.
Typical pricing and lead time
Pricing is scoped per engagement. Contact Nettitude directly for a quote based on your network size and requirements.
What you need to prepare
Prepare a current asset inventory and network topology diagram, and confirm your testing scope boundaries before the initial scoping call.
10. Cyberis
Cyberis is a CREST-accredited cybersecurity consultancy based in the UK, delivering technical security assessments for organisations across a range of sectors. Their team focuses on specialist manual testing rather than relying heavily on automated tooling to generate findings.
What they offer for network penetration testing
Cyberis provides internal and external network penetration testing services covering on-premises infrastructure, cloud environments, and hybrid network setups. Their consultants use manual exploitation techniques alongside structured reconnaissance to map your real attack surface accurately.
How they run a typical engagement
Engagements begin with a scoping call to define targets, testing windows, and rules of engagement before any active testing starts. Cyberis then delivers a risk-rated written report with remediation guidance your technical team can act on directly.
Their manual-first testing approach means findings reflect genuine attacker behaviour rather than a list of automated scanner alerts.
Strengths and trade-offs
CREST accreditation and a strong emphasis on manual testing make Cyberis a credible choice for organisations that need rigorous, certified assessments. The trade-off is that their specialist consultancy model means they operate at a smaller scale than some larger firms on this list.
Best fit for
Cyberis suits mid-market organisations and regulated businesses that want certified, manually driven testing rather than a heavily automated assessment.
Compliance and standards coverage
Their testing supports ISO 27001 and Cyber Essentials Plus preparation, helping you close control gaps before a formal certification review.
Typical pricing and lead time
Pricing is scoped per engagement. Contact Cyberis directly for a quote based on your network size and testing requirements.
What you need to prepare
Prepare a current asset inventory and network diagram, and confirm your testing scope boundaries before your first scoping call.
Next steps
Every provider on this list delivers network penetration testing services that meet a recognised quality benchmark, but the right choice depends on your environment, sector, and what you plan to do with the results. If you need a single, standalone test, a specialist boutique firm may suit you. If you want testing tied directly to ISO 27001 compliance or ongoing managed security, you need a provider that can support both.
Before you reach out to anyone, confirm your testing scope, asset inventory, and compliance objectives. Providers can only give you an accurate quote and timeline if they understand what they are working with from the start.
If you want a partner that combines penetration testing expertise with over 30 years of managed cybersecurity experience and a solution-agnostic approach, TrustedIA is worth a conversation. Get in touch with TrustedIA to discuss your requirements and find out how they can help you secure your network.



