
PCI DSS Penetration Testing Requirements: Scope & Frequency
If your organisation processes, stores, or transmits cardholder data, meeting PCI DSS penetration testing requirements isn’t optional, it’s a core part of staying compliant. Yet many businesses struggle to pin down exactly what’s expected: which systems fall in scope, how often tests must run, and what methodology satisfies an assessor. Getting any of these wrong […]
How To Do Penetration Testing: A Step-By-Step Guide
Most organisations know they should test their defences. Far fewer know where to start. Understanding how to do penetration testing properly, from scoping through to reporting, is the difference between a genuine security assessment and a box-ticking exercise that leaves critical vulnerabilities undiscovered. Penetration testing simulates real-world attacks against your systems, networks, and applications to […]
Penetration Testing Checklist: Steps, Scope, And Reporting
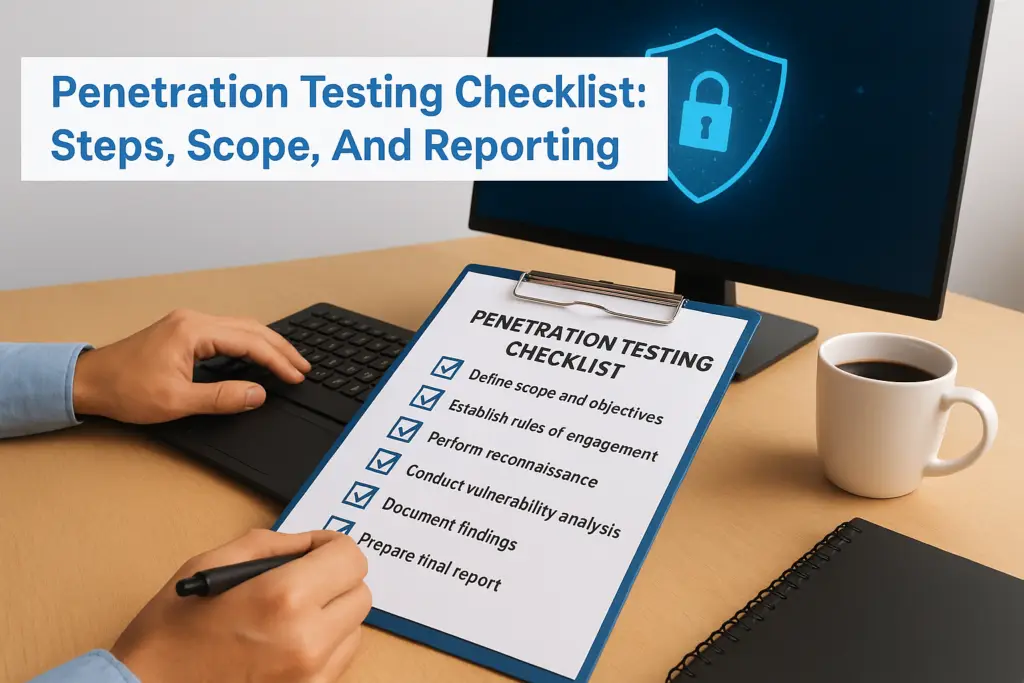
A poorly scoped pen test wastes time, burns budget, and gives you a false sense of security. A well-planned one exposes real vulnerabilities before attackers do. The difference almost always comes down to preparation, and that starts with a solid penetration testing checklist that covers everything from defining scope and rules of engagement to documenting […]
Penetration Testing Steps: A Practical Phase-By-Phase Guide
A penetration test is only as good as the process behind it. Skip a phase, rush the scoping, or treat reporting as an afterthought, and you end up with a tick-box exercise that tells you very little about your actual risk. Understanding the penetration testing steps involved, from the initial planning conversations right through to […]
10 Network Penetration Testing Services In The UK (2026)
Hiring the wrong pen testing provider can give you a false sense of security, or worse, leave critical vulnerabilities undiscovered. With network penetration testing services growing in demand across the UK, choosing a provider that actually understands your infrastructure and compliance requirements matters more than picking the cheapest quote. A thorough test should expose real […]
AWS Penetration Testing Policy: Permitted And Prohibited
Running penetration tests against your AWS-hosted infrastructure without understanding the AWS penetration testing policy can put your organisation at risk, not from attackers, but from AWS itself. Violating their Acceptable Use Policy could lead to service suspension or account termination, which is the opposite of what a security assessment is supposed to achieve. AWS has […]
What Is A Pen Test? Process, Types, And What To Expect
If you’ve ever wondered what is a pen test, the short answer is this: it’s a controlled, simulated attack on your systems designed to find security weaknesses before a real attacker does. Think of it as hiring someone to break into your own business, with your permission, so you can fix the gaps they exploit. […]
NIST Penetration Testing Guidelines: SP 800-115 In Practice
NIST SP 800-115 remains one of the most referenced frameworks for planning and executing security assessments, yet many organisations struggle to translate its guidance into practical, repeatable processes. If you’re searching for NIST penetration testing guidelines, you likely need more than a summary of the document; you need a clear understanding of how to apply […]
