
Cyber Security Governance Principles: A Board-Level Guide
Most boards treat cyber security as a technical problem. It isn’t. A data breach or ransomware attack can wipe out revenue, destroy customer trust, and trigger regulatory action, all of which sit squarely on the board’s agenda. Cyber security governance principles provide the structure boards need to oversee these risks effectively, rather than leaving critical […]
Greenbone Vulnerability Management: Features, OpenVAS & GMP
Knowing what vulnerabilities exist across your network is the first step toward fixing them, and Greenbone Vulnerability Management (GVM) is one of the most widely adopted platforms for doing exactly that. Built on the open-source foundations of OpenVAS, GVM provides organisations with the tools to scan, identify, and prioritise security weaknesses before attackers can exploit […]
Data Security Risk Assessment: A Practical UK 7-Step Guide
Every organisation holds data that someone else wants, customer records, financial information, intellectual property, employee details. A data security risk assessment is the structured process you use to identify what threatens that data, evaluate how likely and damaging each threat is, and decide what to do about it. Without one, you’re making security decisions based […]
How To Do Penetration Testing: A Step-By-Step Guide
Most organisations know they should test their defences. Far fewer know where to start. Understanding how to do penetration testing properly, from scoping through to reporting, is the difference between a genuine security assessment and a box-ticking exercise that leaves critical vulnerabilities undiscovered. Penetration testing simulates real-world attacks against your systems, networks, and applications to […]
12 Cyber Risk Mitigation Strategies Every Business Needs
A single ransomware attack can halt operations for days, drain finances, and erode the trust you’ve spent years building with clients. Yet most businesses still treat cyber security as a reactive problem, something to deal with after things go wrong. Effective cyber risk mitigation strategies flip that approach entirely, giving your organisation a structured way […]
Penetration Testing Checklist: Steps, Scope, And Reporting
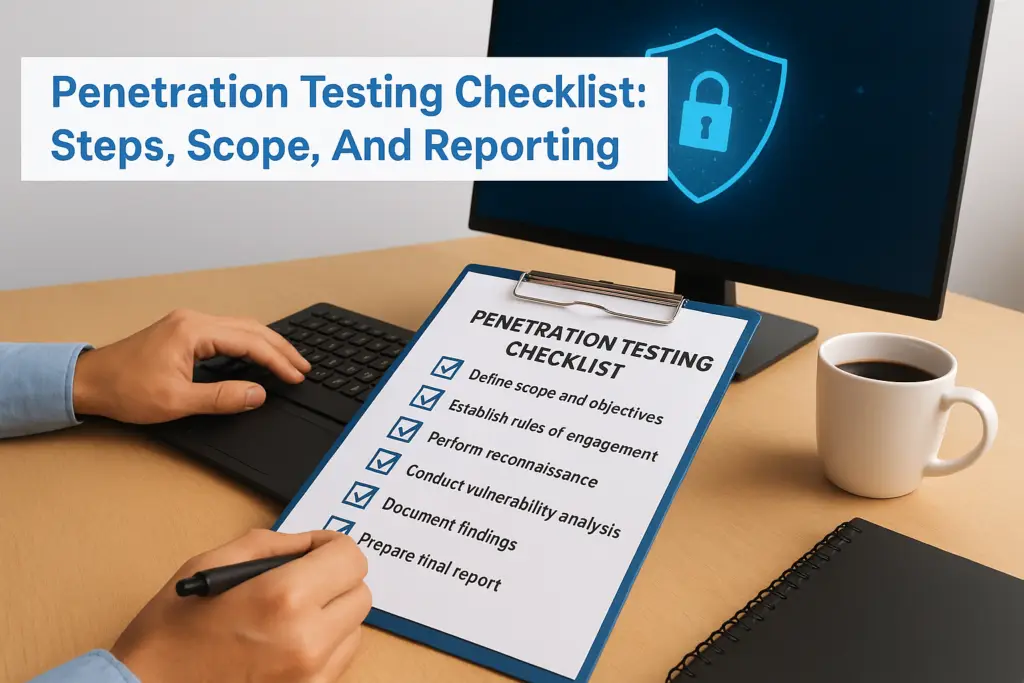
A poorly scoped pen test wastes time, burns budget, and gives you a false sense of security. A well-planned one exposes real vulnerabilities before attackers do. The difference almost always comes down to preparation, and that starts with a solid penetration testing checklist that covers everything from defining scope and rules of engagement to documenting […]
Penetration Testing Steps: A Practical Phase-By-Phase Guide
A penetration test is only as good as the process behind it. Skip a phase, rush the scoping, or treat reporting as an afterthought, and you end up with a tick-box exercise that tells you very little about your actual risk. Understanding the penetration testing steps involved, from the initial planning conversations right through to […]
OWASP Vulnerability Management Guide: How To Build Program
Most organisations know they have vulnerabilities. The harder part is managing them consistently, deciding what to fix first, tracking remediation, and proving progress to stakeholders. That’s exactly the problem the OWASP Vulnerability Management Guide was built to solve. It provides a structured, open-source framework for turning ad hoc scanning into a repeatable programme that actually […]
What Is Cyber Risk Assessment? Steps And Practical Examples
Every organisation holds data that someone else wants, customer records, financial information, intellectual property, operational systems. A cyber risk assessment is the structured process of identifying those assets, pinpointing the threats and vulnerabilities that could compromise them, and determining what the actual impact would be if something went wrong. It’s not a theoretical exercise. It’s […]
Disaster Recovery Consulting Services: What To Expect (UK)
When a ransomware attack encrypts your servers or a critical system failure takes your operations offline, the difference between hours of downtime and days of it often comes down to one thing: how well you planned for it. Disaster recovery consulting services exist to help organisations build, test, and maintain those plans, so recovery isn’t […]
