
Business Continuity Planning Training: What It Is & Why It Matters
A ransomware attack, a flooded server room, a key supplier going bust overnight. None of these wait for a convenient time, and the businesses that recover fastest are the ones where someone actually knew what to do. That’s the gap business continuity planning training closes: it turns a dusty policy document into skills your team […]
Data Protection Officer Services: What They Are & How They Help
If your organisation handles personal data, GDPR probably keeps you up at night. Appointing a Data Protection Officer isn’t optional for many public authorities, large-scale data processors, or businesses handling sensitive information, yet hiring a full-time specialist can cost £60,000 or more a year. That’s why so many IT managers and compliance officers are searching […]
ISO 27001 Compliance vs Certification: What’s the Difference?
You’ve probably heard “ISO 27001 compliant” and “ISO 27001 certified” used as if they mean the same thing. They don’t, and the difference matters when a client, insurer, or tender board asks you to prove it. Understanding iso 27001 compliance vs certification is the first step to picking the right path for your organisation, rather […]
AWS Incident Response Guide: Playbooks, Steps, And Tools
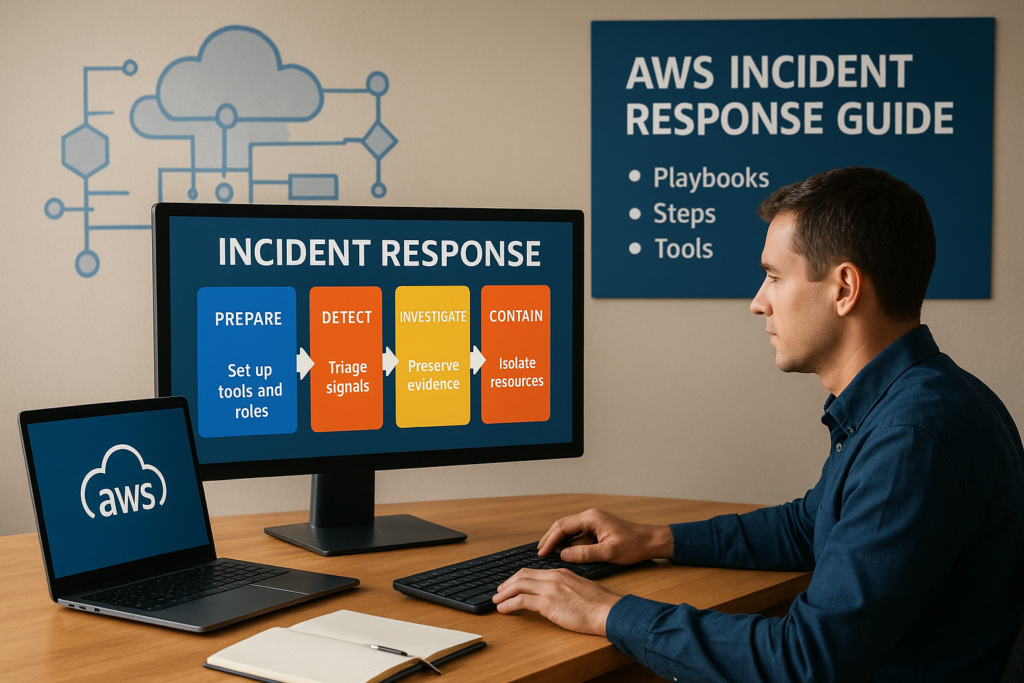
When a security incident hits your AWS environment, the difference between a contained event and a full-blown crisis comes down to preparation. An aws incident response guide isn’t just documentation for the sake of compliance, it’s the operational backbone that tells your team exactly what to do when things go wrong. Yet many organisations running […]
8 Threat Intelligence Services To Strengthen UK Security
Cyber attacks against UK organisations are growing in both frequency and sophistication. Ransomware groups, nation-state actors, and opportunistic criminals don’t announce themselves, they probe, adapt, and exploit gaps before most security teams even notice. That’s where threat intelligence services come in. Rather than waiting for an alert after something has gone wrong, these services give […]
GDPR Compliance For Small Businesses UK: How To Do It Right
Most small business owners know they should be doing something about GDPR compliance for small businesses UK, but "something" often means a privacy policy copied from a competitor and hoping for the best. The problem? The Information Commissioner’s Office (ICO) doesn’t grade on effort. Fines can reach up to £17.5 million or 4% of annual […]
High Availability vs Disaster Recovery: Key Differences
When a critical system goes offline, two questions immediately follow: how quickly can we restore service, and how much data have we lost? The answers depend entirely on whether your organisation has invested in high availability vs disaster recovery, two strategies that are often confused, sometimes conflated, but serve fundamentally different purposes. Understanding the distinction […]
AWS Disaster Recovery Whitepaper: Options, RTO/RPO Guide
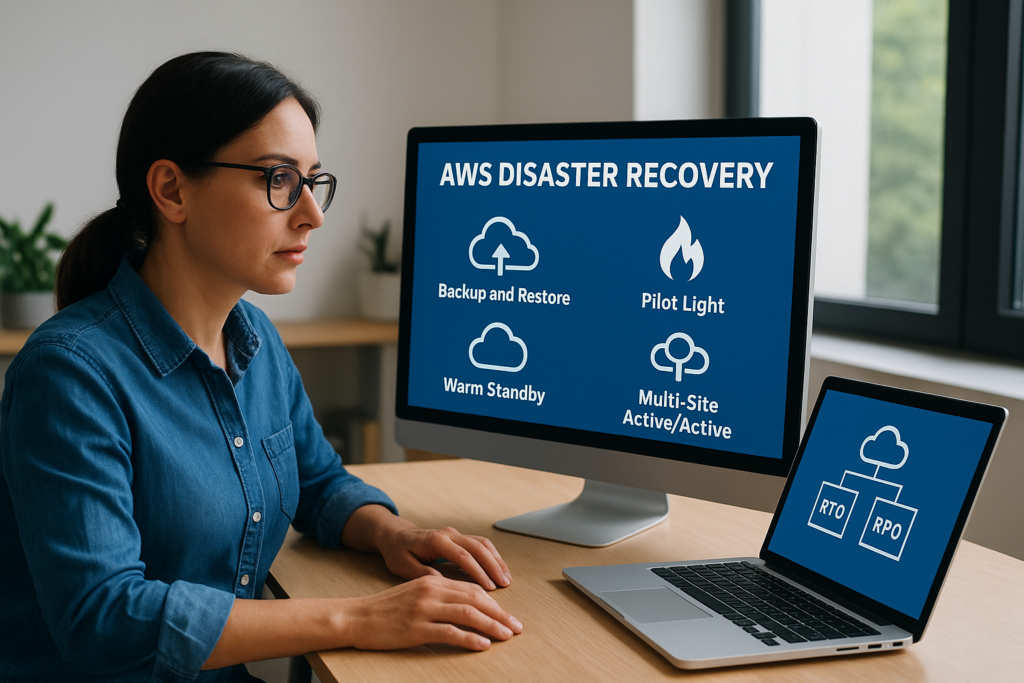
Every organisation running workloads on AWS needs a clear plan for what happens when things go wrong. Hardware fails, regions go dark, ransomware encrypts production databases, and the difference between a brief disruption and a catastrophic loss often comes down to how well your disaster recovery strategy was designed before the incident occurred. The AWS […]
Next Generation Endpoint Security: What It Is And Benefits
Traditional antivirus software relies on signature databases, lists of known threats that need constant updating. The problem? Attackers have moved far beyond what signature-based detection can catch. Fileless malware, zero-day exploits, and polymorphic threats slip past these defences routinely. Next generation endpoint security exists to close that gap, using behavioural analysis, artificial intelligence, and machine […]
PCI DSS Penetration Testing Requirements: Scope & Frequency
If your organisation processes, stores, or transmits cardholder data, meeting PCI DSS penetration testing requirements isn’t optional, it’s a core part of staying compliant. Yet many businesses struggle to pin down exactly what’s expected: which systems fall in scope, how often tests must run, and what methodology satisfies an assessor. Getting any of these wrong […]
