
ISO 27001 Compliance Checklist (XLS): What to Include
Searching for an iso 27001 compliance checklist xls usually means one thing: you’ve been handed the job of getting your organisation certified, and you need a way to track hundreds of requirements without losing your mind in email threads and sticky notes. A spreadsheet still beats most fancy GRC tools for this stage, as long […]
7 Best Incident Response Courses to Build Your Skills
When a breach hits, the gap between a calm, controlled response and total chaos usually comes down to training. That’s why so many IT managers and analysts start searching for incident response courses the moment they realise their team is reacting on guesswork rather than a rehearsed plan. Whether you’re building a career in security […]
How to Get ISO 27001 Certified: Steps, Costs & Timeline
If a client, insurer, or tender document has just asked you to prove ISO 27001 compliance, you’re probably wondering where to even start. Working out how to get ISO 27001 certified isn’t complicated once you know the sequence, but most businesses waste months chasing the wrong first step or paying for consultancy they don’t need […]
Vulnerability Management vs Patch Management: Key Differences
Ask five IT managers to define these two terms and you’ll likely get five different answers, half of which use the words interchangeably. That confusion causes real problems. Teams patch a handful of visible flaws and assume they’re covered, while attackers walk in through gaps nobody scanned for. Understanding vulnerability management vs patch management matters […]
UK GDPR: What It Is and Your Key Obligations
If you handle customer or employee data in the UK, you’re already subject to the UK General Data Protection Regulation, whether you’ve read it or not. Since Brexit, this sits alongside the Data Protection Act 2018 as the legal backbone for how organisations collect, store, and process personal information, and the fines for getting it […]
Cloud Data Protection Services: What They Are & How They Work
Move your data to the cloud and you inherit a new set of risks alongside the convenience. Misconfigured storage buckets, weak access controls, and unmonitored file sharing cause more breaches than sophisticated hacking ever does, and they sit at the top of the most common cloud data security problems we see. If you’re trying to […]
Threat & Vulnerability Management: What It Is & How It Works
Every week brings a fresh batch of CVEs, and most IT teams simply cannot patch everything at once. If you have ever stared at a vulnerability scan with 400 findings and no idea where to start, you already understand why threat & vulnerability management exists. It is the discipline that turns that overwhelming list into […]
Vulnerability Management Dashboards: What They Are & Key Features
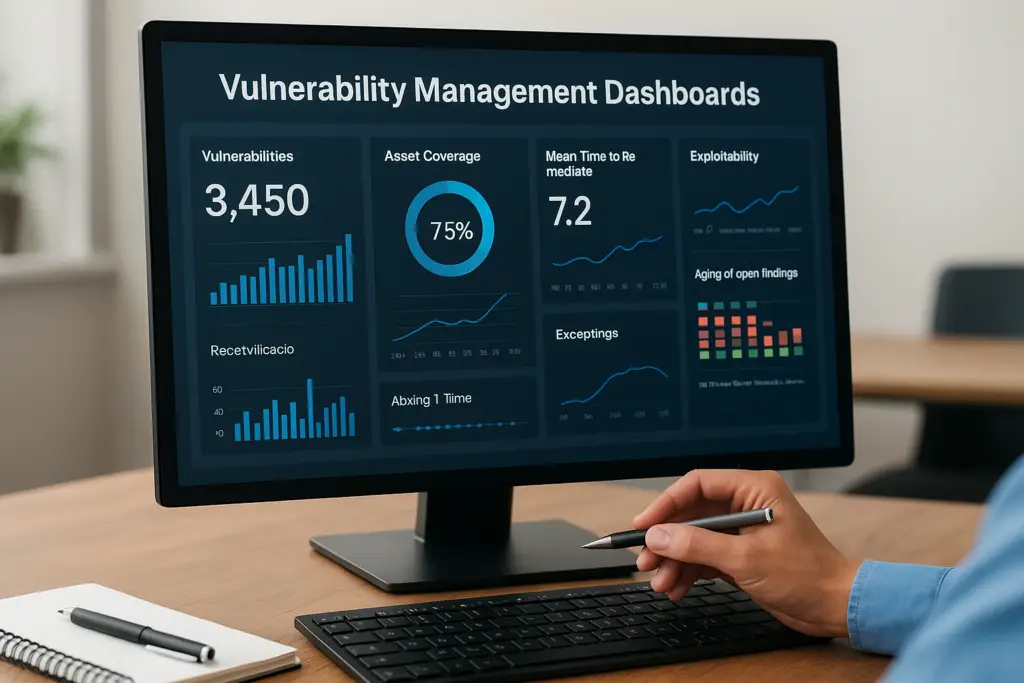
You’ve got a scanner spitting out thousands of findings a month, and someone on your team still has to decide which ones actually matter. That’s the gap vulnerability management dashboards are built to close. Without one, security teams end up buried in spreadsheets, chasing CVE numbers with no real sense of business impact or exploitability. […]
Breaching the Data Protection Act: What It Means and the Consequences
A single misdirected email or an unpatched server can put your organisation on the wrong side of the law. Breaching the Data Protection Act happens more often through carelessness than malice, yet the ICO doesn’t distinguish much between the two when it comes to enforcement. If you’ve had a near miss, a reported incident, or […]
Data Protection Act and the NHS: What It Means for Patients
If you’ve ever handed over your NHS number, medical history, or home address to a GP receptionist, you’ve trusted the NHS with some of the most sensitive data that exists about you. The data protection act nhs relationship isn’t just a legal formality tucked away in a privacy notice. It’s the rulebook that decides who […]
