What Are Managed Security Services?
A security alert at 2.13 am is not just a technical event. For most organisations, it is a business risk that lands long before the working day starts, often without the in-house capacity to assess it quickly or respond with confidence. That is the practical context behind the question: what are managed security services, and […]
The Importance Of Cyber Security Awareness For Employees
Most cyber attacks don’t start with a hacker breaking through a firewall. They start with someone clicking a link in an email, reusing a weak password, or opening a file they shouldn’t have. The importance of cyber security awareness cannot be overstated because the majority of breaches trace back to human error, not technical failure. […]
What Is A Pen Test? Process, Types, And What To Expect
If you’ve ever wondered what is a pen test, the short answer is this: it’s a controlled, simulated attack on your systems designed to find security weaknesses before a real attacker does. Think of it as hiring someone to break into your own business, with your permission, so you can fix the gaps they exploit. […]
RTO And RPO In Disaster Recovery: Definitions And Targets
Every disaster recovery plan hinges on two numbers. If you don’t know yours, you’re guessing, and guessing with downtime and data loss is expensive. RTO and RPO in disaster recovery are the metrics that define how quickly your business must recover and how much data you can afford to lose when something goes wrong. Recovery […]
Network Penetration Testing Guide: Types, Phases, And Tools
A network penetration testing guide matters because too many organisations treat pen testing as a checkbox exercise, something they do once a year to satisfy an auditor, then forget about it until the next review. That approach leaves gaps. Real attackers don’t follow audit schedules, and the businesses that understand this are the ones that […]
Disaster Recovery Explained: Steps, Methods, And RTO/RPO
When a ransomware attack encrypts your files or a server failure takes your operations offline, the clock starts ticking. Every minute of downtime costs money, erodes customer trust, and puts your business at genuine risk. Having disaster recovery explained clearly, and, more importantly, planned properly, is what separates organisations that bounce back from those that […]
7 Cybersecurity Awareness Best Practices For Employees
Most cyber attacks don’t start with a sophisticated hack. They start with someone clicking a link they shouldn’t have, reusing a password, or ignoring an update notification. The reality is that human error accounts for the majority of data breaches, and no firewall or endpoint tool can fully compensate for a team that hasn’t been […]
Datto Managed Security Operation Centre (SOC): Explained
Most businesses don’t have the resources to staff a security operations centre around the clock, and most MSPs don’t either. That’s exactly the gap Datto Managed Security Operation Centre (SOC) is designed to fill. It gives MSPs access to 24/7 threat monitoring, detection, and response without the overhead of building and running a SOC from […]
What Is SOC as a Service? How SOCaaS Works and Benefits
If you’ve ever asked what SOC as a Service is, you’re likely weighing up whether your organisation really needs a full in-house security team monitoring threats around the clock, or whether there’s a smarter, more practical option. The short answer: SOC as a Service (SOCaaS) gives you access to a dedicated Security Operations Centre through […]
ISO 27001 Documentation Requirements: 7 Must-Have Records
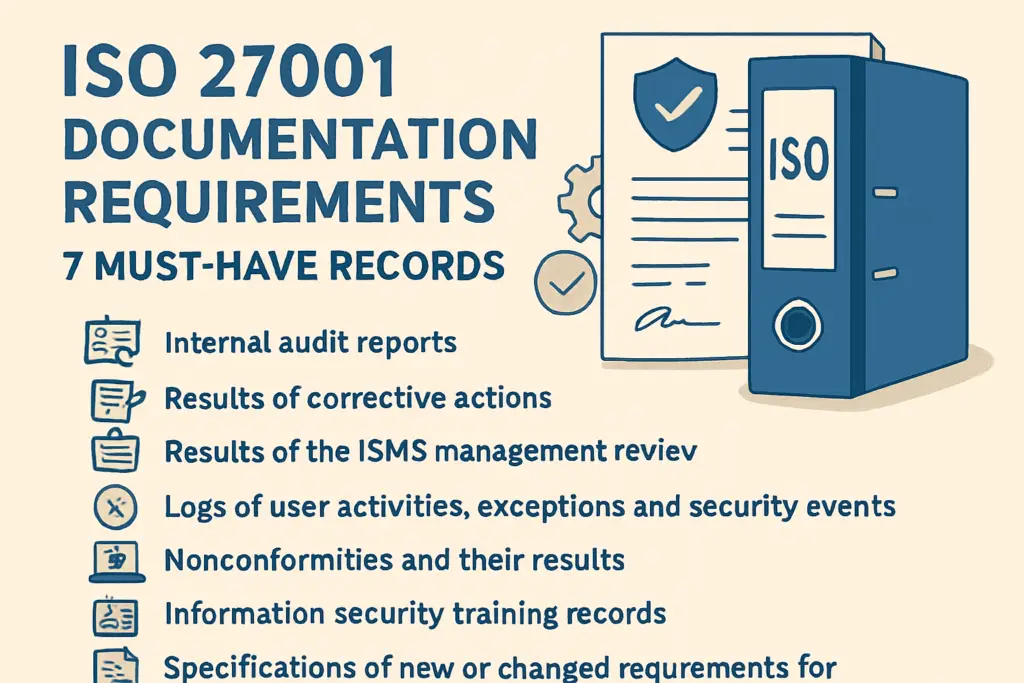
Getting your ISO 27001 documentation requirements right is one of the biggest hurdles organisations face on the path to certification. Miss a single mandatory record, and your audit grinds to a halt. Yet the standard itself isn’t exactly a step-by-step guide; it tells you what to document but leaves the “how” frustratingly open to interpretation. That […]