


ISO 27001 Audit Process: Stages, Steps & How to Prepare
If you’re staring down an ISO 27001 audit process for the first time, the certification stages can feel opaque. Nobody tells you upfront that it’s actually two separate audits, spread weeks apart, each looking for different things. Get either one wrong and you’re back to square one with the certification body, losing months and budget […]
How Does Dark Web Monitoring Work? A Step-By-Step Guide
You’ve probably heard the advice: check if your details are on the dark web. But nobody explains what that actually means in practice. How does dark web monitoring work when the whole point of the dark web is that it’s hidden from normal search engines and browsers? It sounds like guesswork, but it’s actually a […]
Vulnerability Assessment Best Practices: 8 Steps For UK SMEs
Most UK SMEs run a vulnerability scan once, tick a compliance box, and move on. That’s how gaps stay open for months while attackers find them first. If you’re searching for vulnerability assessment best practices, you’ve probably already spotted that scanning tools alone don’t cut it, and you need a repeatable process that actually reduces […]
ISO 27001 Controls Explained: Categories, Numbers & Purpose
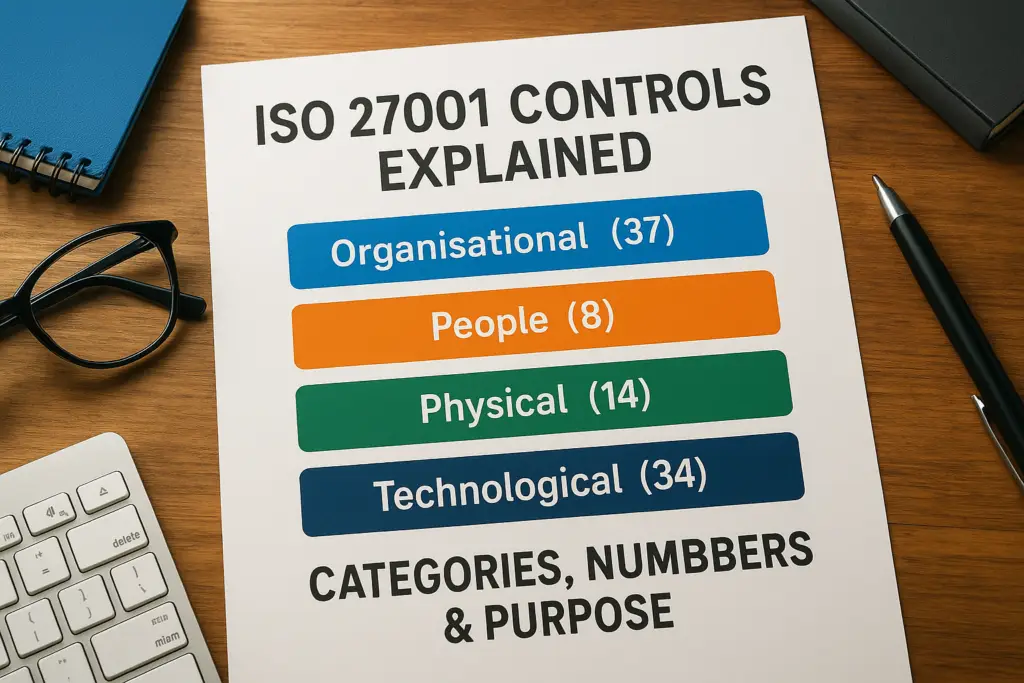
If you’ve opened Annex A of the standard and felt your eyes glaze over at a list of 93 controls, you’re not alone. ISO 27001 controls explained in plain terms is exactly what most IT managers and compliance officers need before they can even start scoping an ISMS, let alone pass an audit. The control […]
Disaster Recovery Plan Best Practices: 8 Steps For UK SMEs
A ransomware attack, a flooded server room, a botched software update. Any one of these can take your systems offline for days, and most UK SMEs never recover the revenue lost in that window. If you’re searching for disaster recovery plan best practices, you’ve probably already had a scare, or you’ve seen what happened to […]
10 Best Endpoint Detection and Response Solutions in 2026
Every laptop, server and mobile device on your network is a potential entry point for an attacker, and antivirus alone stopped being enough years ago. If you’re hunting for the best endpoint detection and response solutions, you’re probably reacting to a near miss, a compliance requirement, or simply the realisation that your current tooling can’t […]
Zero Trust Security Model Explained: How It Works & Principles
Most breaches today do not happen because a firewall failed. They happen because someone already inside the network, a user, a device, or an app, was trusted by default and abused that trust. The zero trust security model flips this old assumption on its head. Instead of granting access based on network location, it demands […]
How to Investigate a Data Breach: Step-By-Step Guide
You’ve just discovered something is wrong. Maybe it’s an unusual login alert, a ransom note on a server, or a phishing report from an employee. Whatever triggered it, you now need to know how to investigate a data breach properly, and you need to move fast without making costly mistakes that damage evidence or breach […]
What Is The Dark Web Explained? How It Works, Uses, Risks
Most people use only a thin slice of the internet. Beneath the surface sits a hidden layer that search engines like Google never index, and understanding what is the dark web explained in plain terms matters more now than ever. It’s a part of the internet that fuels genuine privacy needs and serious criminal activity […]
Zero Trust vs Traditional Security: Differences Explained
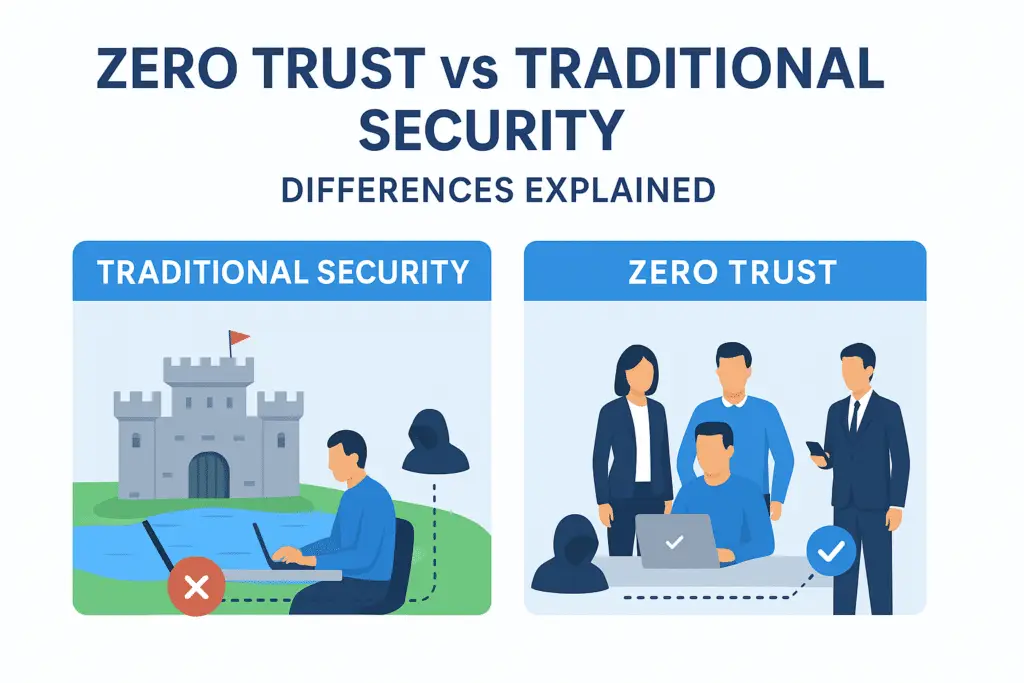
Most businesses still rely on a security model built around a simple idea: trust everything inside the network, block everything outside. That worked when employees sat at office desks and data lived on local servers. But remote work, cloud services, and increasingly sophisticated attacks have exposed serious cracks in that thinking. Understanding zero trust vs […]
