NIST Penetration Testing Guidelines: SP 800-115 In Practice
NIST SP 800-115 remains one of the most referenced frameworks for planning and executing security assessments, yet many organisations struggle to translate its guidance into practical, repeatable processes. If you’re searching for NIST penetration testing guidelines, you likely need more than a summary of the document; you need a clear understanding of how to apply […]
ICO GDPR Guidance: Official UK Resources And Practical Steps
The ICO’s GDPR guidance is the most authoritative resource available to any UK organisation seeking to get data protection right. Published by the Information Commissioner’s Office, the UK’s independent supervisory authority, it covers everything from lawful bases for processing to data breach reporting, individual rights, and accountability obligations. If you handle personal data, this guidance isn’t […]
Network Penetration Testing Guide: Types, Phases, And Tools
A network penetration testing guide matters because too many organisations treat pen testing as a checkbox exercise, something they do once a year to satisfy an auditor, then forget about it until the next review. That approach leaves gaps. Real attackers don’t follow audit schedules, and the businesses that understand this are the ones that […]
Employee Phishing Test: How To Run One Safely, Measure Risk
Most cyber attacks don’t start with a hacker breaking through a firewall. They start with an email, and an employee who clicks the wrong link. An employee phishing test simulates that exact scenario, giving you a controlled way to see how your team responds to a realistic phishing attempt before a real one lands in […]
Cybersecurity Awareness Training For Staff: Complete Guide
Most cyber attacks don’t start with a hacker breaking through a firewall. They start with an employee clicking a link they shouldn’t have. Phishing emails, weak passwords, and mishandled data account for the majority of security breaches, and no amount of technology alone can fix that. This is exactly why cybersecurity awareness training for staff has […]
Disaster Recovery Explained: Steps, Methods, And RTO/RPO
When a ransomware attack encrypts your files or a server failure takes your operations offline, the clock starts ticking. Every minute of downtime costs money, erodes customer trust, and puts your business at genuine risk. Having disaster recovery explained clearly, and, more importantly, planned properly, is what separates organisations that bounce back from those that […]
7 Cybersecurity Awareness Best Practices For Employees
Most cyber attacks don’t start with a sophisticated hack. They start with someone clicking a link they shouldn’t have, reusing a password, or ignoring an update notification. The reality is that human error accounts for the majority of data breaches, and no firewall or endpoint tool can fully compensate for a team that hasn’t been […]
Benefits Of Threat Intelligence: Value, Use Cases, ROI
Most organisations know cyber threats are growing more sophisticated. Fewer know exactly what’s heading their way, or how to act on that knowledge before damage is done. That gap between awareness and action is precisely where the benefits of threat intelligence become clear. Rather than reacting to incidents after they unfold, threat intelligence gives security […]
Datto Antivirus: Features, Reporting, Integrations, And Fit
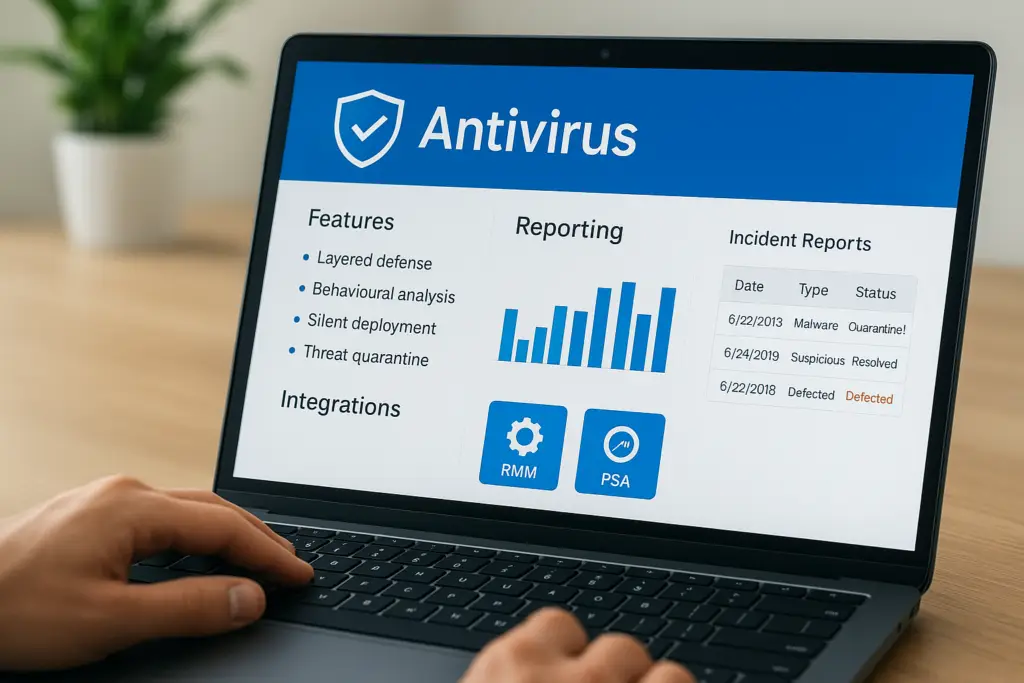
If you manage endpoints across multiple client sites, or even your own, you’ve probably come across Datto Antivirus while evaluating security tools. It’s a product that sits within the broader Datto ecosystem, and understanding what it actually does (and doesn’t do) matters before you commit to rolling it out. Endpoint protection is foundational, but not […]
What Does Cyber Insurance Require?
A renewal questionnaire lands in the inbox, and suddenly the conversation changes. What looked like an insurance purchase becomes a security review. For many organisations, that is the moment the real question appears – what does cyber insurance require, and are we actually ready to answer it with evidence rather than intention? Cyber insurers have […]