
How to Investigate a Data Breach: Step-By-Step Guide
You’ve just discovered something is wrong. Maybe it’s an unusual login alert, a ransom note on a server, or a phishing report from an employee. Whatever triggered it, you now need to know how to investigate a data breach properly, and you need to move fast without making costly mistakes that damage evidence or breach […]
Ransomware Incident Response Steps: A Step-By-Step Guide
A ransomware notice on screen gives you minutes, not hours, to make decisions that affect your entire business. Panic leads to mistakes: paying too fast, wiping evidence, or restoring backups that are already infected. Knowing the ransomware incident response steps before an attack happens is what separates a two-day recovery from a two-week shutdown. This […]
What Is The Dark Web Explained? How It Works, Uses, Risks
Most people use only a thin slice of the internet. Beneath the surface sits a hidden layer that search engines like Google never index, and understanding what is the dark web explained in plain terms matters more now than ever. It’s a part of the internet that fuels genuine privacy needs and serious criminal activity […]
Why Is Business Continuity Planning Important For UK SMEs?
A single ransomware attack can shut down operations for days or even weeks. For UK SMEs, that kind of downtime doesn’t just hurt, it can be fatal. According to the Federation of Small Businesses, around 5.5 million small businesses operate across the UK, and many of them have no formal plan for what happens when […]
How To Respond To A Data Breach: 7-Step Guide For UK SMEs
A data breach can hit without warning, a suspicious login, a ransomware note, or a call from a customer asking why their details are circulating online. In that moment, knowing how to respond to a data breach quickly and correctly is the difference between a contained incident and a full-blown crisis. For UK SMEs, the […]
What Does ISO 27001 Cover? Scope, ISMS, Controls (2022)
ISO 27001 is the internationally recognised standard for information security management, but if you’re trying to figure out what does ISO 27001 cover, the standard itself isn’t exactly light reading. Between the clauses, annexes, and control categories, it’s easy to get lost before you even understand what’s actually required of your organisation. Here’s the short […]
Zero Trust vs Traditional Security: Differences Explained
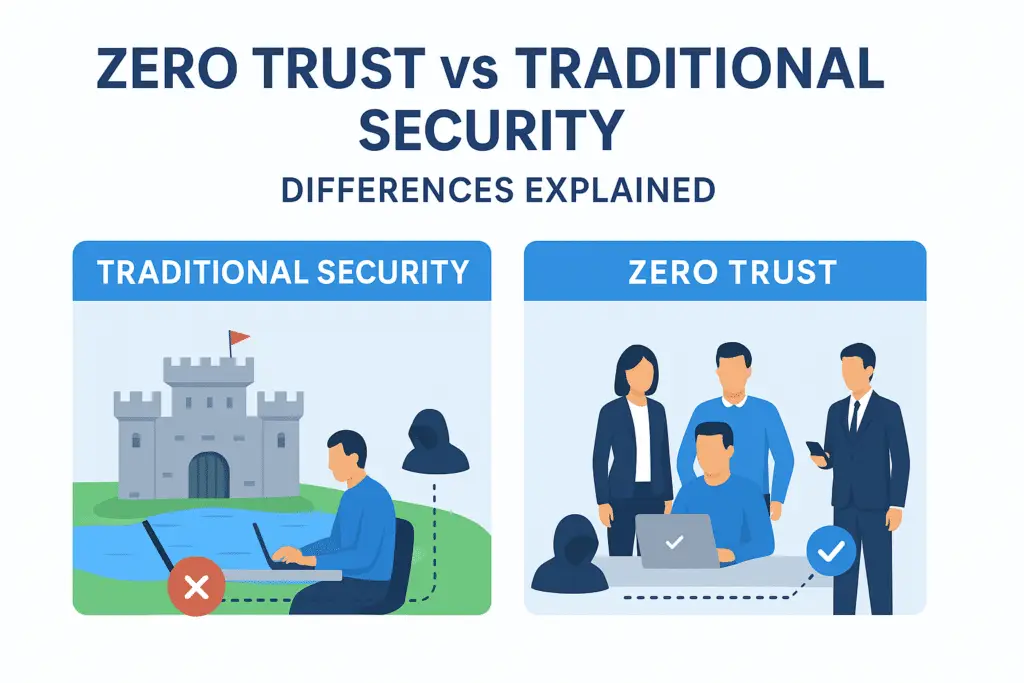
Most businesses still rely on a security model built around a simple idea: trust everything inside the network, block everything outside. That worked when employees sat at office desks and data lived on local servers. But remote work, cloud services, and increasingly sophisticated attacks have exposed serious cracks in that thinking. Understanding zero trust vs […]
Zero Trust Security Benefits: 9 Business And Security Gains
Traditional perimeter-based security operates on a simple assumption: everything inside the network is safe. That assumption has been failing businesses for years. Credentials get stolen, endpoints get compromised, and attackers move laterally through networks with little resistance. The zero trust security benefits address this head-on by flipping the model, no user, device, or application is […]
ISO 27001 For Small Businesses: Steps, Costs & Timeline
Most small business owners assume ISO 27001 is built for large corporations with dedicated security teams and six-figure budgets. That assumption costs them contracts. We’ve seen it firsthand, companies losing deals because a prospective client or supply chain partner asked for proof of ISO 27001 for small businesses, and they had nothing to show. The […]
Cyber Security Strategy Framework: Step-By-Step Guide
Most organisations know they need better cyber security. Fewer know where to start. A cyber security strategy framework gives you that starting point, a structured, repeatable approach to identifying risks, setting priorities, and building defences that actually hold up when tested. Without one, security efforts tend to be reactive, patchy, and expensive. With one, every […]
