


Ransomware Incident Response Steps: A Step-By-Step Guide
A ransomware notice on screen gives you minutes, not hours, to make decisions that affect your entire business. Panic leads to mistakes: paying too fast, wiping evidence, or restoring backups that are already infected. Knowing the ransomware incident response steps before an attack happens is what separates a two-day recovery from a two-week shutdown. This […]
How To Respond To A Data Breach: 7-Step Guide For UK SMEs
A data breach can hit without warning, a suspicious login, a ransomware note, or a call from a customer asking why their details are circulating online. In that moment, knowing how to respond to a data breach quickly and correctly is the difference between a contained incident and a full-blown crisis. For UK SMEs, the […]
Incident Response Communications Plan: How To Build One
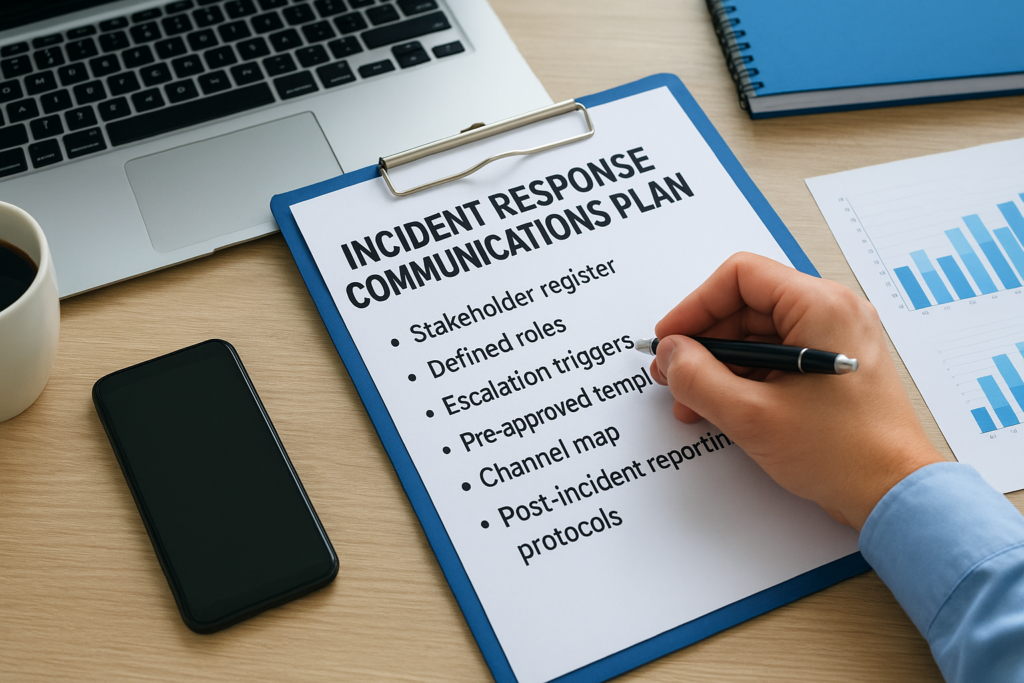
A cyber attack hits your organisation. Your security team jumps into action, containment protocols kick in, and technical recovery begins. But within minutes, the real chaos starts, employees panic, customers demand answers, regulators expect notifications, and journalists start calling. Without a solid incident response communications plan, even a well-handled technical response can spiral into reputational […]
Incident Response Training For Employees: UK How-To Guide
Most UK businesses don’t discover gaps in their cyber incident response until something goes wrong. By then, the cost, financial, operational, and reputational costs have already started climbing. The reality is that incident response training for employees isn’t a nice-to-have checkbox; it’s the difference between a contained security event and a full-blown crisis. And yet, […]
Disaster Recovery Explained: Steps, Methods, And RTO/RPO
When a ransomware attack encrypts your files or a server failure takes your operations offline, the clock starts ticking. Every minute of downtime costs money, erodes customer trust, and puts your business at genuine risk. Having disaster recovery explained clearly, and, more importantly, planned properly, is what separates organisations that bounce back from those that […]
What Does Cyber Insurance Require?
A renewal questionnaire lands in the inbox, and suddenly the conversation changes. What looked like an insurance purchase becomes a security review. For many organisations, that is the moment the real question appears – what does cyber insurance require, and are we actually ready to answer it with evidence rather than intention? Cyber insurers have […]
Incident Response Roles And Responsibilities Explained
When a cyber incident hits, the difference between a controlled recovery and chaos often comes down to one thing: whether your team knows exactly who does what. Clearly defined incident response roles and responsibilities aren’t just a box-ticking exercise; they’re the backbone of every effective response plan. Without them, critical actions get duplicated, missed, or […]
NIST Computer Security Incident Handling Guide: Key Steps
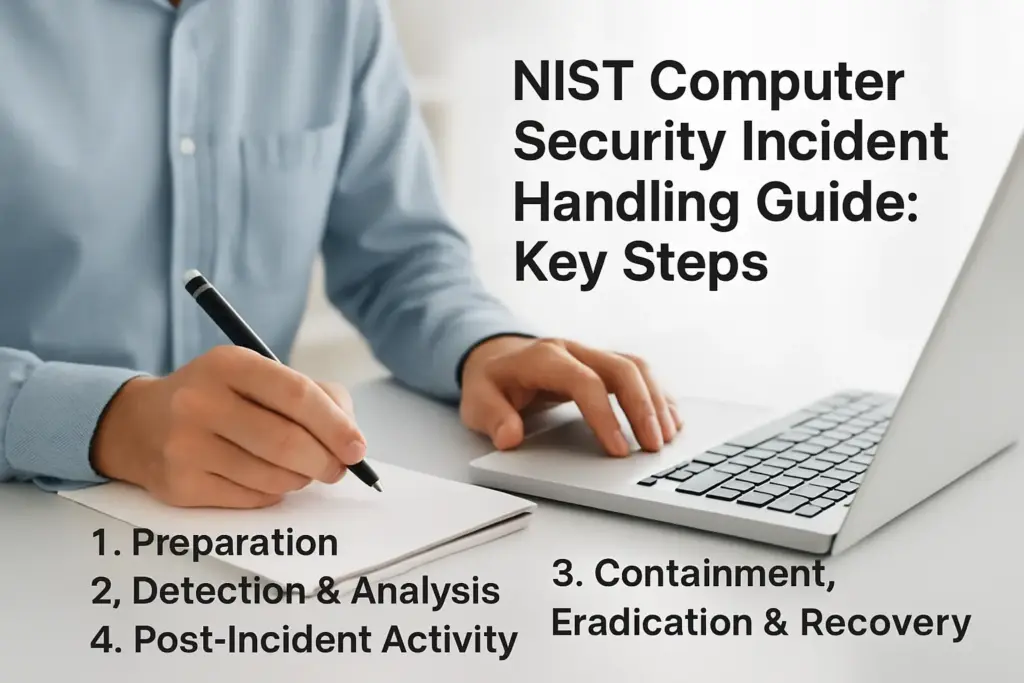
When a security incident hits, the difference between a contained disruption and a full-blown crisis often comes down to one thing: how well your response plan holds up under pressure. The NIST Computer Security Incident Handling Guide (Special Publication 800-61) is the most widely referenced framework for building that plan. It gives organisations a structured, […]
Incident Response Checklist: Steps To Prepare And Recover
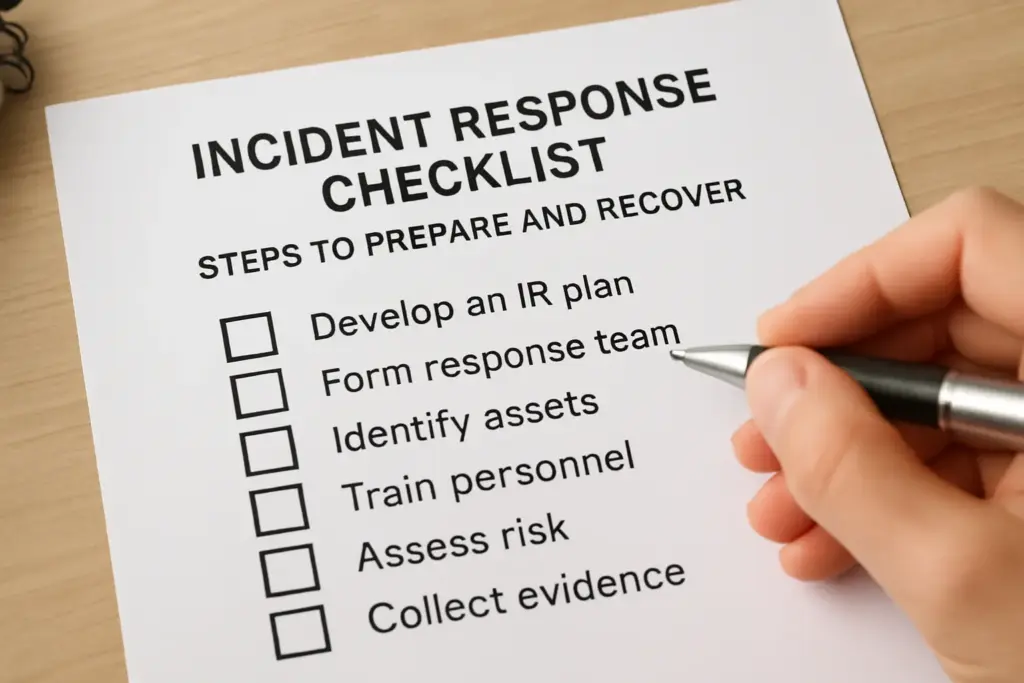
A cyber attack doesn’t announce itself on your schedule. It hits when your team is least prepared, and the difference between a contained incident and a full-blown crisis often comes down to one thing: whether you had a plan ready to execute. An incident response checklist gives your organisation a plan, a clear, repeatable sequence […]
How To Build An Effective Incident Response Framework
Every business today faces the risk of a cyber incident—sometimes from a sophisticated attacker, sometimes from a simple oversight. The difference between a minor disruption and a full-blown crisis often comes down to how well an organisation is prepared to respond. High-profile breaches like WannaCry and the Target attack have shown that the true cost […]
