FCA Business Continuity Requirements: SYSC Rules Explained
If your firm is regulated by the Financial Conduct Authority, you’re expected to have more than a vague plan for when things go wrong. FCA business continuity requirements are set out clearly in the Senior Management Arrangements, Systems and Controls (SYSC) sourcebook, primarily under SYSC 4.1 and SYSC 13.8, and they leave little room for […]
Incident Response Roles And Responsibilities Explained
When a cyber incident hits, the difference between a controlled recovery and chaos often comes down to one thing: whether your team knows exactly who does what. Clearly defined incident response roles and responsibilities aren’t just a box-ticking exercise; they’re the backbone of every effective response plan. Without them, critical actions get duplicated, missed, or […]
How To Create A Business Continuity Plan: Step-By-Step
A single cyber incident, a server room flood, or a key supplier going offline can bring operations to a grinding halt. The difference between a business that recovers quickly and one that doesn’t usually comes down to one thing: whether they planned for it. Knowing how to create a business continuity plan gives you a […]
ISO 27001 Certification: How To Achieve It Step-By-Step
Getting ISO 27001 certified is one of the strongest signals you can send to clients, partners, and regulators that your organisation takes information security seriously. But figuring out how to achieve ISO 27001 certification, from scoping your Information Security Management System (ISMS) to passing the Stage 2 audit, can feel overwhelming, especially if you’re doing […]
How To Implement Data Governance: A Step-By-Step Roadmap
Most organisations don’t struggle with data governance because they lack ambition. They struggle because no one owns it, no one defines it clearly, and everyone assumes someone else is handling it. The result? Duplicated data, inconsistent policies, compliance gaps, and security blind spots that leave the business exposed. Understanding how to implement data governance properly […]
ISO 27001 Documentation Requirements: 7 Must-Have Records
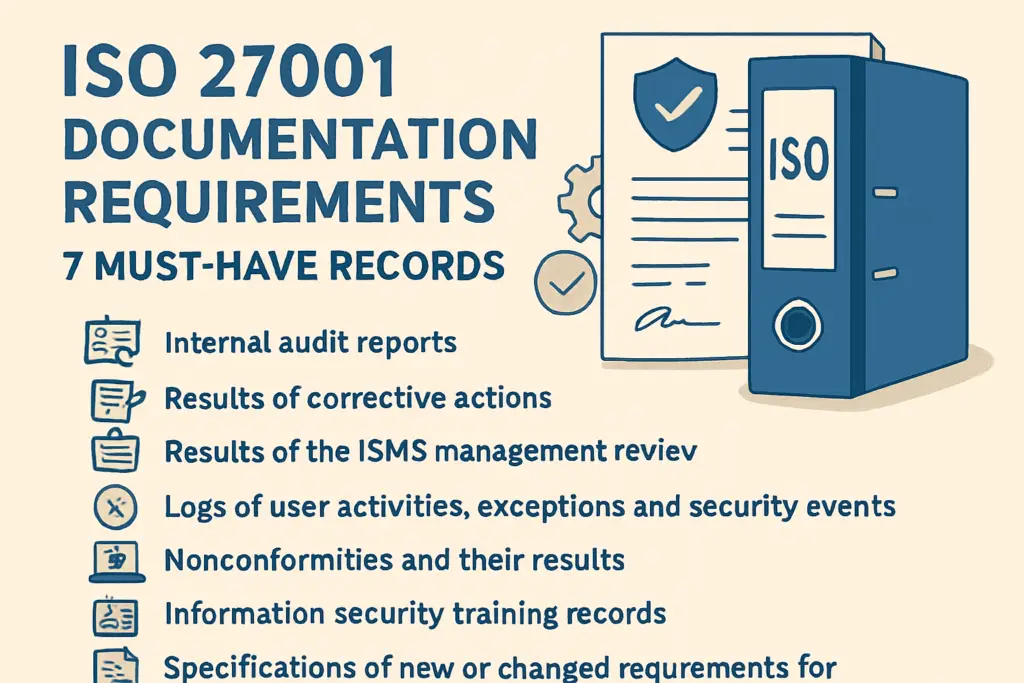
Getting your ISO 27001 documentation requirements right is one of the biggest hurdles organisations face on the path to certification. Miss a single mandatory record, and your audit grinds to a halt. Yet the standard itself isn’t exactly a step-by-step guide; it tells you what to document but leaves the “how” frustratingly open to interpretation. That […]
NIST Computer Security Incident Handling Guide: Key Steps
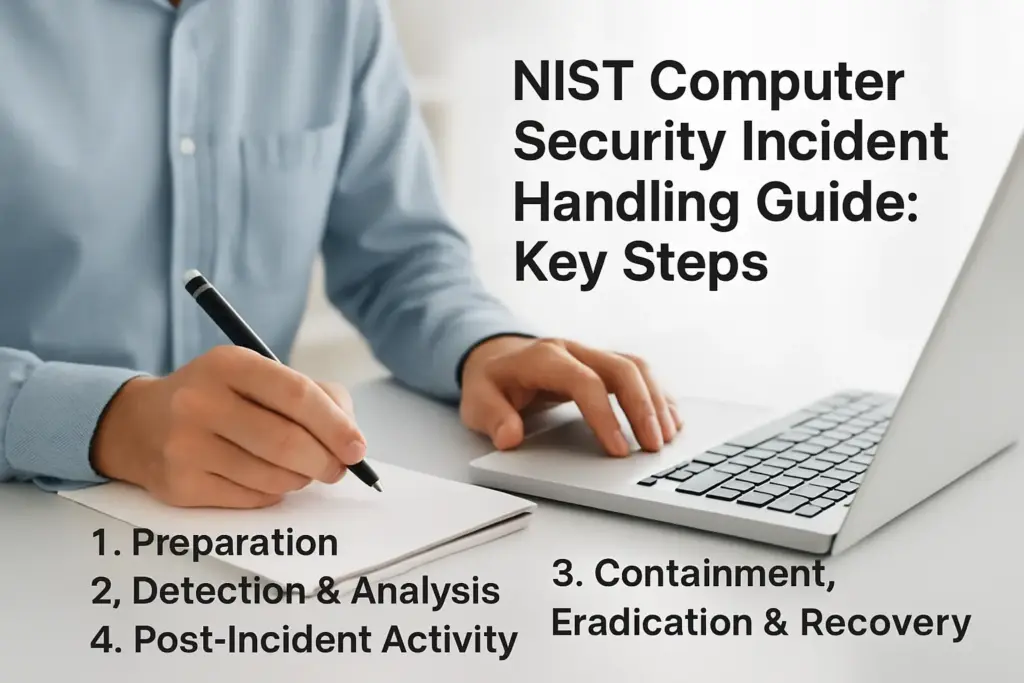
When a security incident hits, the difference between a contained disruption and a full-blown crisis often comes down to one thing: how well your response plan holds up under pressure. The NIST Computer Security Incident Handling Guide (Special Publication 800-61) is the most widely referenced framework for building that plan. It gives organisations a structured, […]
Incident Response Checklist: Steps To Prepare And Recover
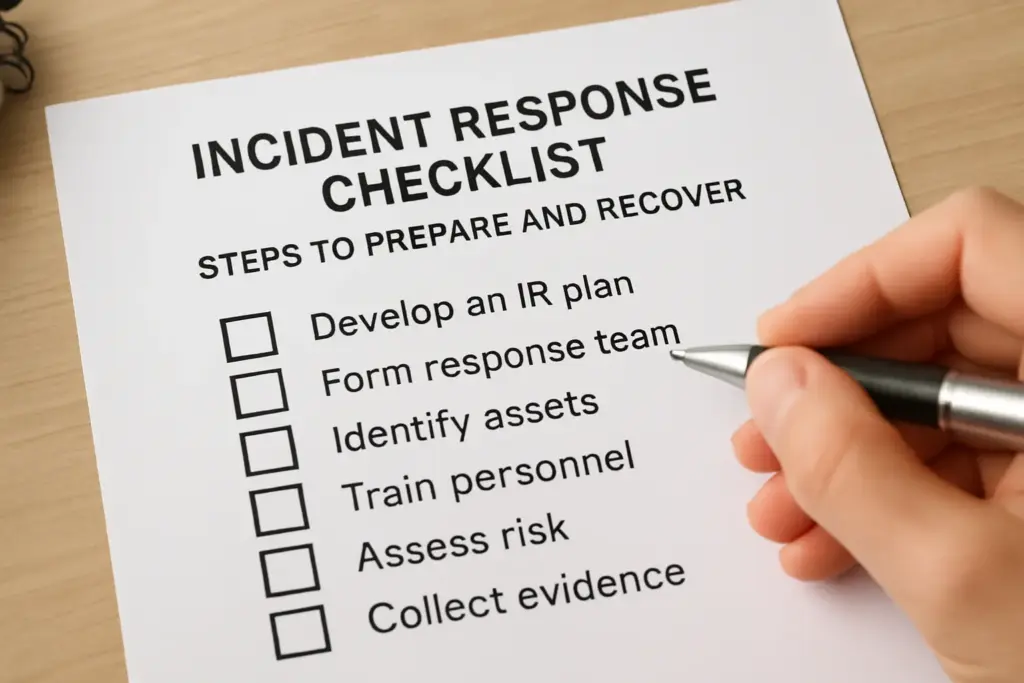
A cyber attack doesn’t announce itself on your schedule. It hits when your team is least prepared, and the difference between a contained incident and a full-blown crisis often comes down to one thing: whether you had a plan ready to execute. An incident response checklist gives your organisation a plan, a clear, repeatable sequence […]
How To Build An Effective Incident Response Framework
Every business today faces the risk of a cyber incident—sometimes from a sophisticated attacker, sometimes from a simple oversight. The difference between a minor disruption and a full-blown crisis often comes down to how well an organisation is prepared to respond. High-profile breaches like WannaCry and the Target attack have shown that the true cost […]
7 Types Of Cyber Security Audits Every Business Should Know
Cyber attacks have become more relentless and sophisticated, catching even well-prepared organisations off guard. Last year alone, nearly a third of UK businesses reported a cybersecurity breach or attack, with regulatory fines and reputational fallout rising for those who failed to meet compliance requirements. For IT leaders, business owners, and compliance professionals, the challenge is […]