


Security Operations Centre (SOC): Definition: Roles, Tools, And Team
A security operations centre definition might sound straightforward, a team that monitors and responds to cyber threats. But the reality behind those words involves a layered operation of people, processes, and technology working around the clock to keep businesses running. Getting that definition right matters, because understanding what a SOC actually does is the first […]
EDPB GDPR Guidelines: What They Are And Where To Find Them
The GDPR is a dense piece of legislation, and the regulation itself doesn’t always spell out how its rules should be applied in practice. That’s where the EDPB GDPR guidelines come in. The European Data Protection Board regularly publishes guidance documents that clarify how specific provisions of the GDPR should be interpreted, covering everything from […]
What Is A Cyber Security Strategy? Components And Examples
Every organisation faces cyber threats, from ransomware attacks that halt operations to data breaches that erode customer trust. The difference between those who recover quickly and those who don’t often comes down to one thing: whether they had a plan in place before the incident. Understanding what a cybersecurity strategy is matters because it’s the […]
What Is ISO 22301: BCMS Standard, Benefits & Certification
Every business faces disruptions, from cyberattacks and supply chain failures to power outages and natural disasters. The difference between organisations that recover quickly and those that struggle for weeks often comes down to preparation. So, what is ISO 22301, and why should it be on your radar? It’s the internationally recognised standard that provides a […]
GDPR Compliance Checklist: 7 Steps For UK Businesses In 2026
Getting GDPR right isn’t optional, and the fines prove it. The UK Information Commissioner’s Office (ICO) continues to hold organisations accountable, with penalties reaching into the millions for mishandling personal data. Whether you’re processing customer records, employee information, or supplier details, having a solid GDPR compliance checklist is the difference between confidence and costly mistakes. […]
The Complete Guide To GDPR Gap Analysis Service For SMEs
Most SMEs know they need to comply with GDPR, but few can pinpoint exactly where their gaps are. A GDPR gap analysis service gives you that clarity, a structured assessment that maps your current data protection practices against the regulation’s requirements and identifies the specific areas where you fall short. Without it, you’re essentially guessing […]
Incident Response Communications Plan: How To Build One
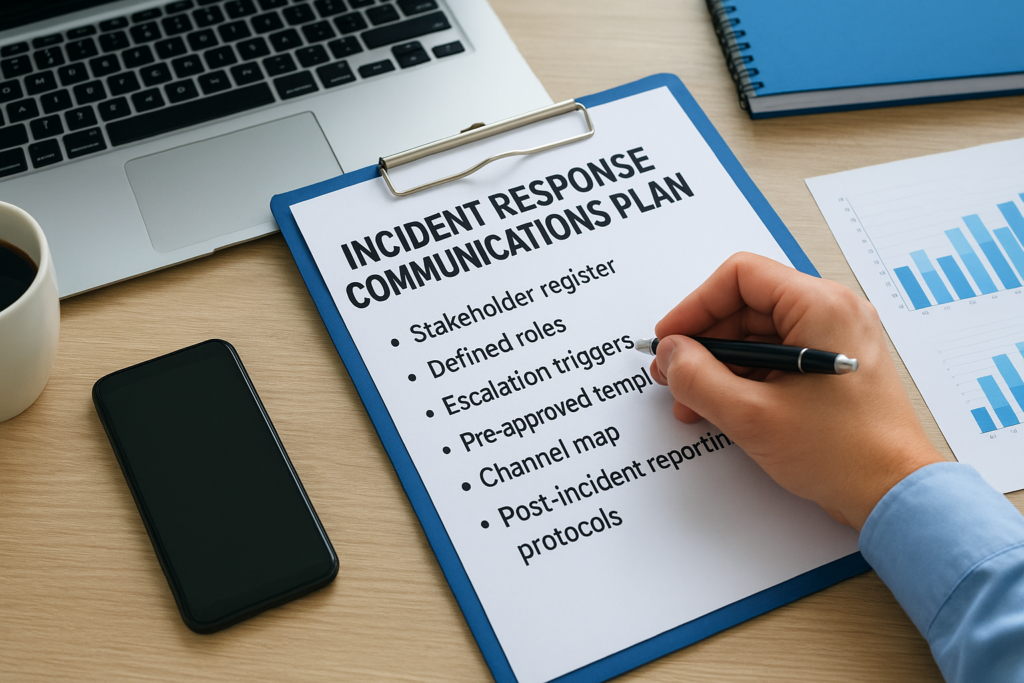
A cyber attack hits your organisation. Your security team jumps into action, containment protocols kick in, and technical recovery begins. But within minutes, the real chaos starts, employees panic, customers demand answers, regulators expect notifications, and journalists start calling. Without a solid incident response communications plan, even a well-handled technical response can spiral into reputational […]
10 Cloud Data Security Challenges And How To Overcome Them
More organisations than ever store sensitive data in the cloud, but moving data off-premises doesn’t mean the risks disappear. If anything, cloud data security challenges have grown more complex as businesses adopt multi-cloud environments, hybrid architectures, and SaaS platforms, scattering critical information across dozens of providers. A single misconfigured storage bucket or overlooked access policy […]
Role Of The Data Protection Officer Under GDPR Explained
Every organisation that processes personal data under the GDPR needs to understand the data protection officer’s role, even if it’s not legally required to appoint one. The DPO sits at the intersection of compliance, risk management, and operational decision-making, serving as an independent point of accountability for how your business handles personal data. But the role […]
European Commission Standard Contractual Clauses: Overview
When your organisation transfers personal data to a processor or another controller, especially one based outside the European Economic Area, you need a lawful mechanism to protect that data. European Commission Standard Contractual Clauses (SCCs) are one of the most widely used tools for exactly this purpose, providing pre-approved contractual safeguards that align with GDPR […]
