Last Updated: 29 October 2026
Quick Summary
ISO 27001 implementation means building an Information Security Management System (ISMS) that meets the standard’s requirements, then proving it through independent certification. For UK companies, it involves documenting how you protect information, managing risk systematically and demonstrating that discipline to clients, regulators and insurers.
- Scope is where most implementations quietly fail, so draw the ISMS boundary carefully and justify exclusions.
- Certification body fees are invoiced at Stage 1, Stage 2 and each surveillance audit, so cash flow is lumpy.
- Every Annex A control must be implemented or justified as excluded in the Statement of Applicability.
- Choose a UKAS-accredited certification body, as accreditation is what buyers check in tenders.
- Certification runs a three-year cycle with surveillance audits in years one and two, then recertification.
Table of Contents
- What ISO 27001 Implementation Means for UK Businesses
- The ISO 27001 Implementation Timeline: A Phase-by-Phase Plan
- Defining the Scope and Building Your Risk Treatment Plan
- ISO 27001 Certification Cost UK: Budgeting for the Full Cycle
- The ISO 27001 Mandatory Documentation List and Annex A Controls
- Your ISO 27001 Internal Audit Checklist and Management Review
- Aligning ISO 27001 with UK GDPR and Choosing a UKAS-Accredited Certification Body
- Maintaining Certification After the Audit: Surveillance and Continuous Improvement
- Frequently Asked Questions
What ISO 27001 Implementation Means for UK Businesses
ISO 27001 implementation is the process of building an Information Security Management System (ISMS) that meets the requirements of the international standard, then proving it through independent certification.
Many SMEs and mid-market firms pursue certification without hiring a full-time security executive.
The commercial driver is usually a tender or client questionnaire. Buyers in regulated sectors increasingly treat certification as a baseline expectation.
Below, we break down each phase, what it costs in time and money, and where firms lose months.
The ISO 27001 Implementation Timeline: A Phase-by-Phase Plan
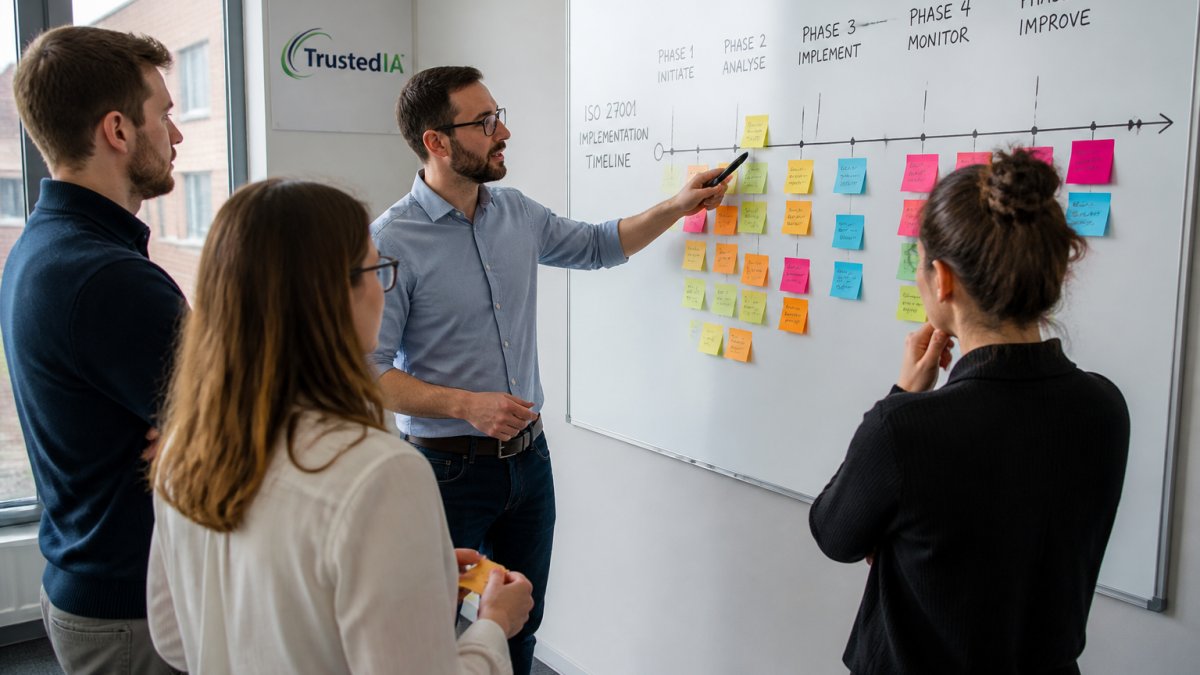
A realistic ISO 27001 implementation timeline depends on organisation size, scope and how much documentation already exists. Typical stages follow this sequence:
- Scoping and gap analysis (3-6 weeks): define the ISMS boundary, identify existing controls, list what is missing.
- Risk assessment and treatment plan (4-8 weeks): identify assets, score risks, choose controls.
- Documentation build (6-10 weeks): policies, procedures, the Statement of Applicability.
- Control implementation (8-16 weeks, overlaps with documentation): technical and organisational controls.
- Internal audit and management review (3-4 weeks): test the system, fix findings.
- Stage 1 and Stage 2 certification audits (4-8 weeks including scheduling).
Typical Durations for SMEs and Mid-Market Firms
| Phase | SME (under 50 staff) | Mid-market (50-250 staff) |
|---|---|---|
| Scoping and gap analysis | 3-4 weeks | 5-6 weeks |
| Risk assessment and treatment | 4-6 weeks | 6-8 weeks |
| Documentation build | 6-8 weeks | 8-10 weeks |
| Control implementation | 8-12 weeks | 12-16 weeks |
| Internal audit and review | 3 weeks | 4 weeks |
| Certification audits | 4-6 weeks | 6-8 weeks |
Defining the Scope and Building Your Risk Treatment Plan
Scope is where most implementations quietly fail.
Start with the context of the organisation: what you do, who you serve, what contractual and legal obligations apply, and which information assets carry risk.
Your risk assessment should follow a repeatable method. Identify assets, identify threats and vulnerabilities, score likelihood and impact, then decide treatment: mitigate, transfer, avoid or accept.
The risk treatment plan feeds directly into the Statement of Applicability (SoA), which maps each Annex A control to your decision. If you are unsure where you stand before scoping, an ISO 27001 gap analysis establishes the baseline.
A common mistake is treating the risk assessment as a one-off document. It is a living register.
ISO 27001 Certification Cost UK: Budgeting for the Full Cycle
ISO 27001 certification cost in the UK depends on organisation size, scope complexity and whether you use consultants. For current pricing or a quote tailored to your organisation, contact TrustedIA directly.
Where the Money Goes: Certification Body, Tools and Internal Time
Four cost lines dominate:
- Certification body fees. Based on audit days, which scale with headcount and scope. Expect Stage 1 and Stage 2 audits in year one, then annual surveillance audits.
- Consultancy and implementation support. Optional, but it can compress timelines and reduce the risk of a failed Stage 2.
- Tooling. ISMS platforms, vulnerability scanning, endpoint protection, logging.
Budgeting only for the certification body and ignoring internal hours is the most common cause of abandoned programmes. Build the internal time estimate before you commit, and treat it as a real cost even though it does not appear on an invoice.
The Trade-Offs That Move the Number
Three decisions swing the budget more than anything else:
- Scope breadth. Every system and location inside the ISMS boundary adds audit days and control evidence. Scoping tightly and justifying exclusions in the Statement of Applicability is the biggest lever on certification body fees.
- Consultancy versus self-implementation. Consultancy costs money but can save time and reduce the risk of a failed Stage 2.
- Tooling versus spreadsheets. A GRC platform reduces manual evidence-gathering but adds a recurring licence. Many SMEs run the first cycle on structured spreadsheets and move to a platform once the ISMS is stable.
Planning the Cash Flow
Certification body fees are typically invoiced at Stage 1, Stage 2 and each surveillance audit, so cash flow is lumpy. Consultancy is usually staged against milestones; tooling is annual and often paid upfront. Build a 36-month cash-flow view, not a single-year budget: the year-three recertification audit is larger than the surveillance audits before it.
The ISO 27001 Mandatory Documentation List and Annex A Controls
The standard requires a defined set of documented information. You do not need a policy for everything, but you do need these:
- Scope of the ISMS
- Information security policy
- Risk assessment methodology and results
Annex A provides the control catalogue, organised into organisational, people, physical and technological themes. ISO 27002 explains how each control is typically implemented. You need not implement every control, but every exclusion must be justified in the SoA.
Tracking this against a spreadsheet gets unwieldy fast. A structured ISO 27001 checklist spreadsheet keeps the mandatory documentation and Annex A mapping in one auditable place.
Your ISO 27001 Internal Audit Checklist and Management Review
The internal audit is where you find your own problems before the certification body does. It must be planned, independent of the work being audited, and documented.
A workable internal audit checklist covers:
- Is the scope statement current and accurate?
- Has the risk assessment been reviewed since the last audit cycle?
- Does the SoA match the risk treatment plan?
Management review follows: leadership examines audit results, risk trends, incidents and objectives, then records decisions.
If you lack the independence to audit your own work, a cybersecurity audit service can conduct or support the review.
Aligning ISO 27001 with UK GDPR and Choosing a UKAS-Accredited Certification Body
ISO 27001 and UK GDPR overlap heavily but are not interchangeable. ISO 27001 gives you a management system for information security; UK GDPR and the Data Protection Act 2018 impose specific legal obligations around lawful processing, data subject rights and breach notification. The Information Commissioner’s Office guidance on data protection is the authoritative reference for the legal side, and its principles map cleanly onto Annex A controls for access management, encryption and incident response.
How the Two Regimes Actually Map
The overlap is real but partial, and understanding where they diverge is what stops you running two compliance programmes by accident:
- Risk assessment. ISO 27001 requires an information security risk assessment; UK GDPR requires a data protection impact assessment (DPIA) for high-risk processing. Different documents, but they can share one asset inventory and one risk register with a data-protection lens applied.
- Access control. Annex A’s access control theme maps directly onto UK GDPR’s integrity and confidentiality principle.
- Incident response. ISO 27001 requires an incident management process; UK GDPR requires notifiable personal data breaches to reach the ICO within 72 hours. One incident process should feed both, with a data-protection triage step.
Run them together: one asset inventory, one risk register, one incident process, one supplier register. Separate compliance programmes duplicate effort and create contradictions, for example, an incident classified as ‘low’ under the ISMS but notifiable to the ICO. A combined approach to ISO 27001 and GDPR compliance is the single highest-leverage UK-specific decision in the whole programme.
Build the data-protection lens into the risk assessment from day one rather than bolting it on afterwards. Retrofitting a DPIA process into a mature ISMS is far more disruptive than designing for both from the start.
Choosing a UKAS-Accredited Certification Body
On the certification body: choose one accredited by UKAS. Accreditation is your assurance that the audit was conducted to a recognised standard, and it is what buyers check. An unaccredited certificate may be cheaper but carries materially less weight in tenders and client questionnaires.
Ask these questions before signing:
- Sector experience. Has the auditor worked with firms in your sector? A generic auditor spends more days getting up to speed, which you pay for.
- Audit day allocation. How many days are quoted for Stage 1 and Stage 2, and how were they calculated? Allocation should reflect headcount, scope and complexity.
- Surveillance scheduling. When will surveillance audits fall, and can they align with your internal audit cycle?
A useful approach is to shortlist two or three UKAS-accredited bodies, request quotes against the same scope statement, and compare price, audit day allocation and sector experience.
Maintaining Certification After the Audit: Surveillance and Continuous Improvement
Certification is a three-year cycle. You will face surveillance audits in years one and two, then a recertification audit in year three.
Maintenance is lighter than implementation but not trivial. Expect to keep the risk register current, run internal audits annually, hold management reviews, close nonconformities and evidence continual improvement.
Tooling helps: automated asset discovery, centralised logging and an ISMS platform reduce the manual burden of proving controls still operate. So does having someone who owns the programme.
Frequently Asked Questions
How long does ISO 27001 implementation take for a UK business?
Most SMEs with limited in-house security resource need six to twelve months from kick-off to certification audit. The ISO 27001 implementation timeline depends on scope, existing controls and how quickly staff can complete risk assessments and documentation. Firms with a mature information security management system may finish more quickly, while larger or multi-site organisations typically need longer. Building in extra time for internal audit and management review before the stage two audit is essential.
What are the mandatory documents required for ISO 27001?
The ISO 27001 mandatory documentation list includes the scope of the ISMS, the information security policy, risk assessment and risk treatment methodology, the Statement of Applicability, the risk treatment plan, and evidence of competence and awareness. You also need documented information required by Annex A controls you have selected, plus internal audit results and management review minutes. The standard does not demand a fixed set of policies beyond these, so tailor the list to your scope and risk profile rather than copying a generic template.
How much does ISO 27001 certification cost in the UK?
ISO 27001 certification cost UK varies with organisation size, scope and certification body. Budget for certification body fees, any tooling or consultancy support, and internal staff time. Certification bodies quote based on audit days, which rise with headcount and complexity. Accredited and non-accredited bodies may differ in price, but accreditation matters if clients or regulators expect it. Get at least two quotes and ask what is included in stage one and stage two audits before committing.
Do UK companies need UKAS-accredited certification for ISO 27001?
UKAS accreditation is not a legal requirement, but many UK buyers and public sector tenders expect it. A certificate from a UKAS-accredited certification body carries more weight because the body itself is independently assessed. If your customers are in regulated sectors or you bid for government contracts, choose an accredited body. For internal improvement purposes, a non-accredited certificate may suffice, but check client requirements first to avoid re-certifying later.
How does ISO 27001 align with the UK GDPR?
ISO 27001 provides a framework for managing information security risks, which supports UK GDPR accountability and security obligations. The standard’s risk assessment and Annex A controls help demonstrate appropriate technical and organisational measures. However, ISO 27001 certification does not prove UK GDPR compliance on its own. You still need lawful bases, data subject rights processes and breach notification procedures. Map your ISMS controls to UK GDPR requirements to avoid gaps between the two frameworks.
What should be on an ISO 27001 internal audit checklist?
An ISO 27001 internal audit checklist should cover the ISMS scope, leadership commitment, risk assessment and treatment records, Statement of Applicability, Annex A control implementation, documented information control, competence and awareness, incident management, business continuity and supplier security. Include checks for previous nonconformities and whether corrective actions were closed. Schedule the audit before management review so findings feed into the review agenda. Keep audit evidence, as certification bodies will ask to see it.
Certification stalls for predictable reasons: unclear scope, an unmaintained risk register, and no one with the capacity to own the programme. TrustedIA provides on-demand expert cybersecurity capacity, 24/7 CyberSOS incident response and vCISO advisory that integrates into your existing infrastructure, so ISO 27001 implementation moves without a full-time executive hire. Get started with TrustedIA and build a compliance programme your board can defend.