
8 Threat Intelligence Services To Strengthen UK Security
Cyber attacks against UK organisations are growing in both frequency and sophistication. Ransomware groups, nation-state actors, and opportunistic criminals don’t announce themselves, they probe, adapt, and exploit gaps before most security teams even notice. That’s where threat intelligence services come in. Rather than waiting for an alert after something has gone wrong, these services give […]
PCI DSS Penetration Testing Requirements: Scope & Frequency
If your organisation processes, stores, or transmits cardholder data, meeting PCI DSS penetration testing requirements isn’t optional, it’s a core part of staying compliant. Yet many businesses struggle to pin down exactly what’s expected: which systems fall in scope, how often tests must run, and what methodology satisfies an assessor. Getting any of these wrong […]
OWASP Vulnerability Management Guide: How To Build Program
Most organisations know they have vulnerabilities. The harder part is managing them consistently, deciding what to fix first, tracking remediation, and proving progress to stakeholders. That’s exactly the problem the OWASP Vulnerability Management Guide was built to solve. It provides a structured, open-source framework for turning ad hoc scanning into a repeatable programme that actually […]
5 Best Dark Web Monitoring Services for UK Businesses
Your credentials, customer records, or supplier logins could be circulating on criminal forums right now, and you’d have no idea until fraud, ransomware, or a regulator’s letter lands on your desk. That gap between breach and discovery is exactly what the best dark web monitoring services are built to close, scanning hidden marketplaces and forums […]
How Does Dark Web Monitoring Work? A Step-By-Step Guide
You’ve probably heard the advice: check if your details are on the dark web. But nobody explains what that actually means in practice. How does dark web monitoring work when the whole point of the dark web is that it’s hidden from normal search engines and browsers? It sounds like guesswork, but it’s actually a […]
What Is The Dark Web Explained? How It Works, Uses, Risks
Most people use only a thin slice of the internet. Beneath the surface sits a hidden layer that search engines like Google never index, and understanding what is the dark web explained in plain terms matters more now than ever. It’s a part of the internet that fuels genuine privacy needs and serious criminal activity […]
10 Network Penetration Testing Services In The UK (2026)
Hiring the wrong pen testing provider can give you a false sense of security, or worse, leave critical vulnerabilities undiscovered. With network penetration testing services growing in demand across the UK, choosing a provider that actually understands your infrastructure and compliance requirements matters more than picking the cheapest quote. A thorough test should expose real […]
AWS Penetration Testing Policy: Permitted And Prohibited
Running penetration tests against your AWS-hosted infrastructure without understanding the AWS penetration testing policy can put your organisation at risk, not from attackers, but from AWS itself. Violating their Acceptable Use Policy could lead to service suspension or account termination, which is the opposite of what a security assessment is supposed to achieve. AWS has […]
Types Of Data Security Threats: Examples And Prevention Tips
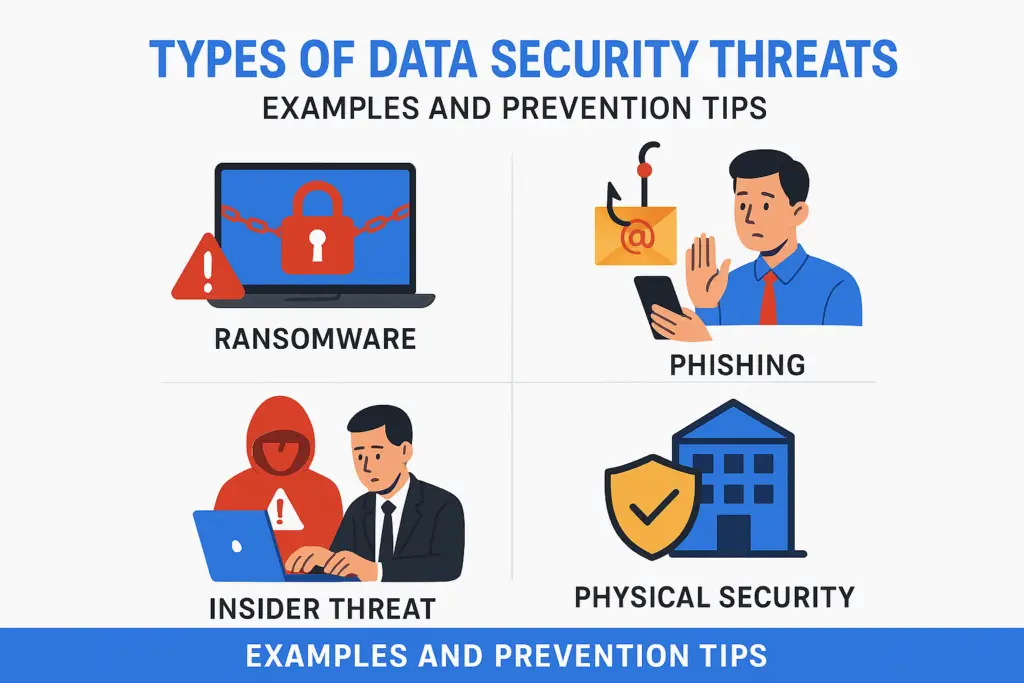
Every organisation holds data that someone else wants, customer records, financial information, intellectual property, credentials. The types of data security threats targeting that information have grown more varied and more damaging over the past decade. From ransomware that locks entire networks to phishing emails that trick a single employee into handing over login details, each […]
What Is A Pen Test? Process, Types, And What To Expect
If you’ve ever wondered what is a pen test, the short answer is this: it’s a controlled, simulated attack on your systems designed to find security weaknesses before a real attacker does. Think of it as hiring someone to break into your own business, with your permission, so you can fix the gaps they exploit. […]
