
ISO 27001 Compliance vs Certification: What’s the Difference?
You’ve probably heard “ISO 27001 compliant” and “ISO 27001 certified” used as if they mean the same thing. They don’t, and the difference matters when a client, insurer, or tender board asks you to prove it. Understanding iso 27001 compliance vs certification is the first step to picking the right path for your organisation, rather […]
ISO 27001 Compliance Checklist (XLS): What to Include
Searching for an iso 27001 compliance checklist xls usually means one thing: you’ve been handed the job of getting your organisation certified, and you need a way to track hundreds of requirements without losing your mind in email threads and sticky notes. A spreadsheet still beats most fancy GRC tools for this stage, as long […]
ISO 27001 vs ISO 27002: What Is the Difference?
If you’ve started researching information security standards, you’ve likely hit the same wall every IT manager and compliance officer hits: the ISO 27001 vs ISO 27002 question. Both numbers get thrown around in the same breath, often as if they’re interchangeable. They’re not, and mixing them up can cost you time and money during an […]
Incident Response Plan Template: What to Include & How to Build One
You searched for an incident response plan template because you need something practical, not another glossy PDF full of theory. Maybe an auditor flagged the gap, a client asked for proof you have one, or you’ve just watched another business get hit by ransomware and realised you’d be improvising if it happened to you. Whatever […]
How to Maintain ISO 27001 Certification: 8 Best Practices
Getting your ISO 27001 certificate is the easy part. Working out how to maintain ISO 27001 certification through three years of surveillance audits, staff turnover, and shifting risks is where most organisations struggle. Certificates get suspended not because businesses fail to care about security, but because nobody owned the ongoing admin once the champagne wore […]
ISO 27001 Audit Process: Stages, Steps & How to Prepare
If you’re staring down an ISO 27001 audit process for the first time, the certification stages can feel opaque. Nobody tells you upfront that it’s actually two separate audits, spread weeks apart, each looking for different things. Get either one wrong and you’re back to square one with the certification body, losing months and budget […]
ISO 27001 Controls Explained: Categories, Numbers & Purpose
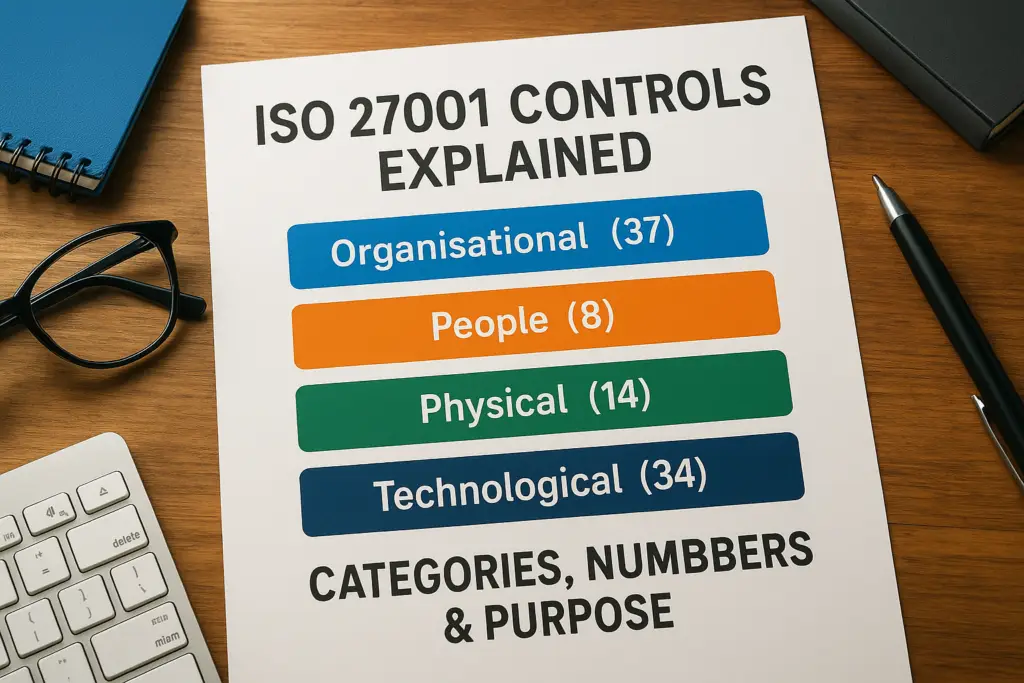
If you’ve opened Annex A of the standard and felt your eyes glaze over at a list of 93 controls, you’re not alone. ISO 27001 controls explained in plain terms is exactly what most IT managers and compliance officers need before they can even start scoping an ISMS, let alone pass an audit. The control […]
What Does ISO 27001 Cover? Scope, ISMS, Controls (2022)
ISO 27001 is the internationally recognised standard for information security management, but if you’re trying to figure out what does ISO 27001 cover, the standard itself isn’t exactly light reading. Between the clauses, annexes, and control categories, it’s easy to get lost before you even understand what’s actually required of your organisation. Here’s the short […]
ISO 27001 For Small Businesses: Steps, Costs & Timeline
Most small business owners assume ISO 27001 is built for large corporations with dedicated security teams and six-figure budgets. That assumption costs them contracts. We’ve seen it firsthand, companies losing deals because a prospective client or supply chain partner asked for proof of ISO 27001 for small businesses, and they had nothing to show. The […]
UK GDPR vs EU GDPR Differences: What Changed Post-Brexit?
When the UK left the EU, data protection law didn’t simply carry over unchanged. The UK GDPR vs EU GDPR differences might seem minor on the surface, but for businesses operating across both jurisdictions, they create real compliance headaches. Understanding exactly what shifted, and what stayed the same, is essential if you want to avoid […]
